RockCloud-基石云安全-官方博客
只是一个默认分类

Nginx Anti-CC Attack Rate Limiting Best Practices: Should You Limit Connections or Requests First?
Discover the best practices for configuring Nginx to defend against CC attacks, combining connection limits, request rate limiting, burst handling, and whitelist exemptions.
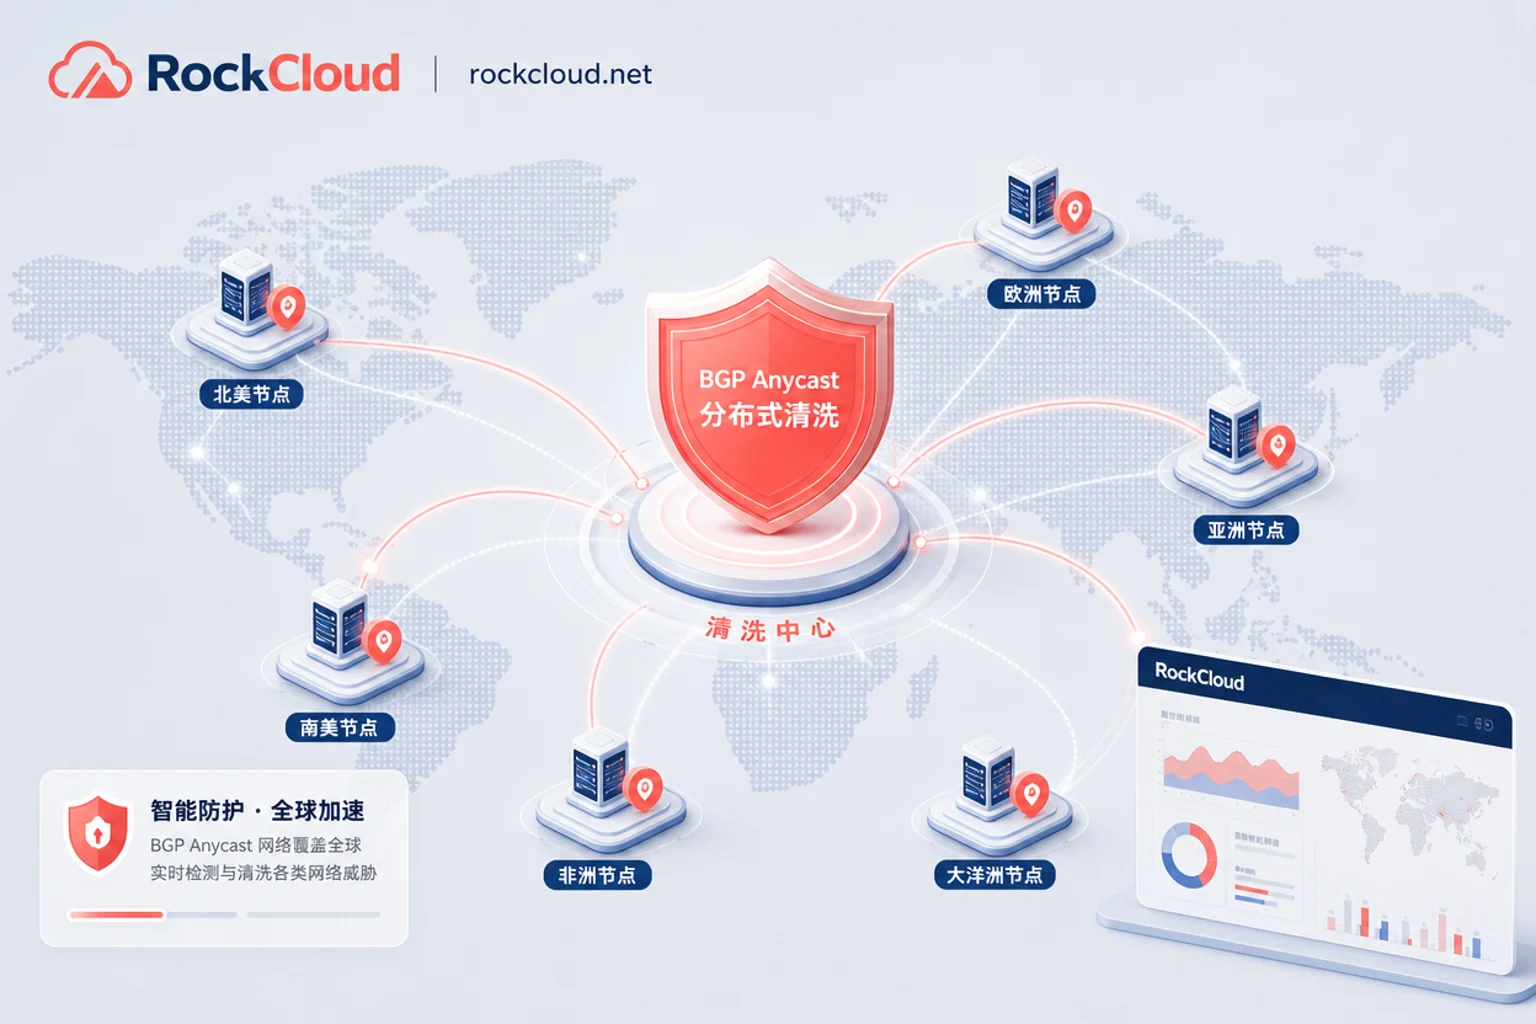
How to Verify BGP Anycast Technology in DDoS Mitigation
A practical guide to verifying BGP Anycast technology in DDoS mitigation through three self-testable links: route announcement, edge local drop, and node removal convergence.

How to Choose High-Protection CDN? Six Criteria to Self-Test Before Signing
Learn the six key criteria to evaluate high-protection CDN providers before signing, beyond nominal defense peaks.
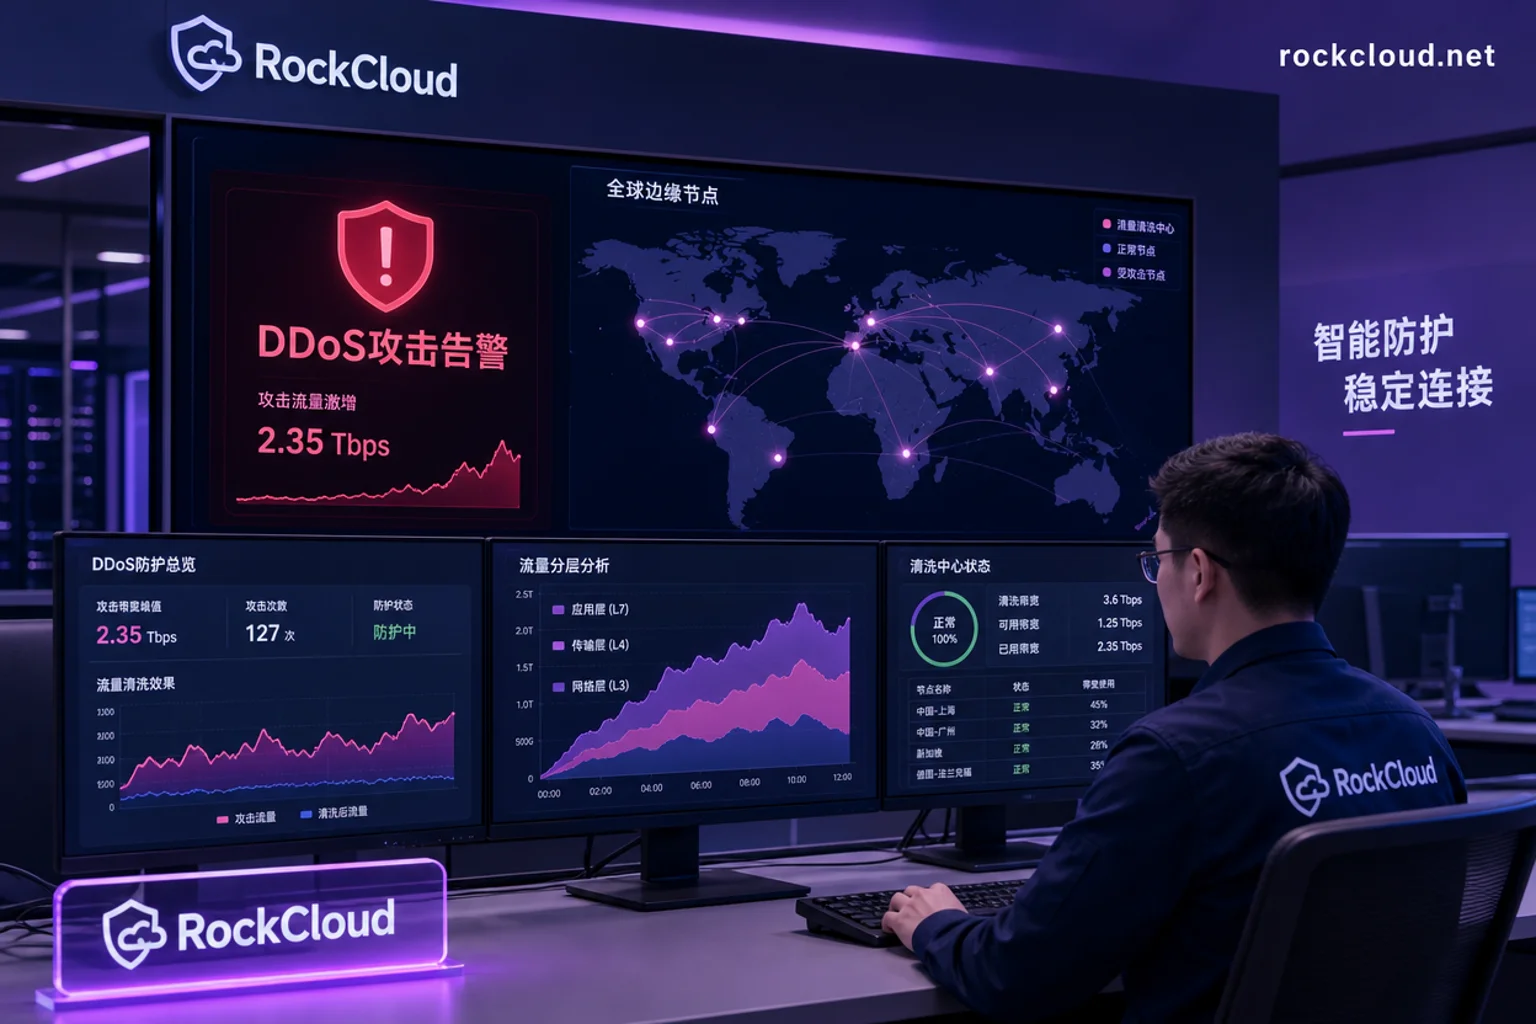
How to Handle DDoS Emergency Response? The Order of Operations Before and After Blackholing
A time-based 4-step DDoS emergency response playbook, covering attack confirmation, traffic diversion, blackhole handling, and post-recovery review, with practical checklists.

BGP High-Protection vs Single-Line High-Protection: Differences and Selection Guide for Enterprise Quotation Comparison
Understand the key differences between BGP and single-line DDoS protection, focusing on routing control and mitigation authority, with a practical comparison table and selection checklist.