RockCloud-基石云安全-官方博客
RockCloud Blog
Insights on cloud security, DDoS protection, CDN acceleration and reliable infrastructure.
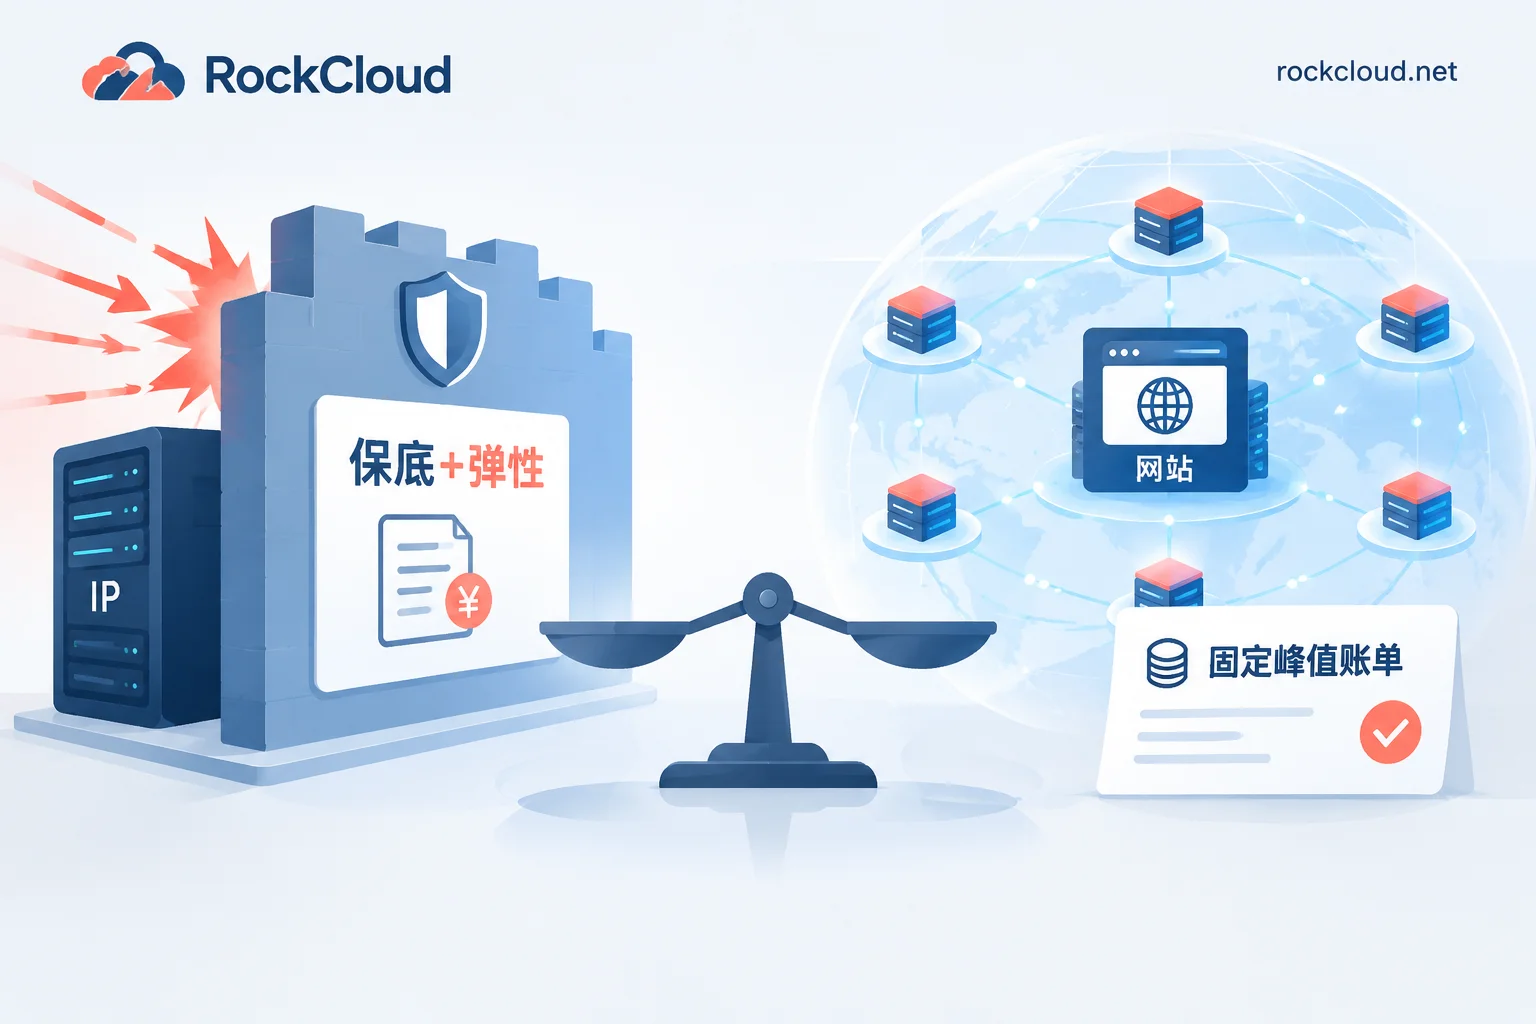
High-Defense IP vs. High-Defense CDN: Which Is Cheaper? Check Business Protocol First, Then Calculate Base, Elastic, and Acceleration Costs
For web and API businesses, high-defense CDN usually has lower initial and long-term costs than high-defense IP. For Layer 4 TCP/UDP businesses like games and long connections, ordinary high-defense CDN cannot be used, leaving only high-defense IP or game shield. This article breaks down the billing items of both, points out common overspending like high-defense IP elastic protection fees and CDN billed by traffic being inflated by CC attacks, and lists questions to ask when getting quotes.
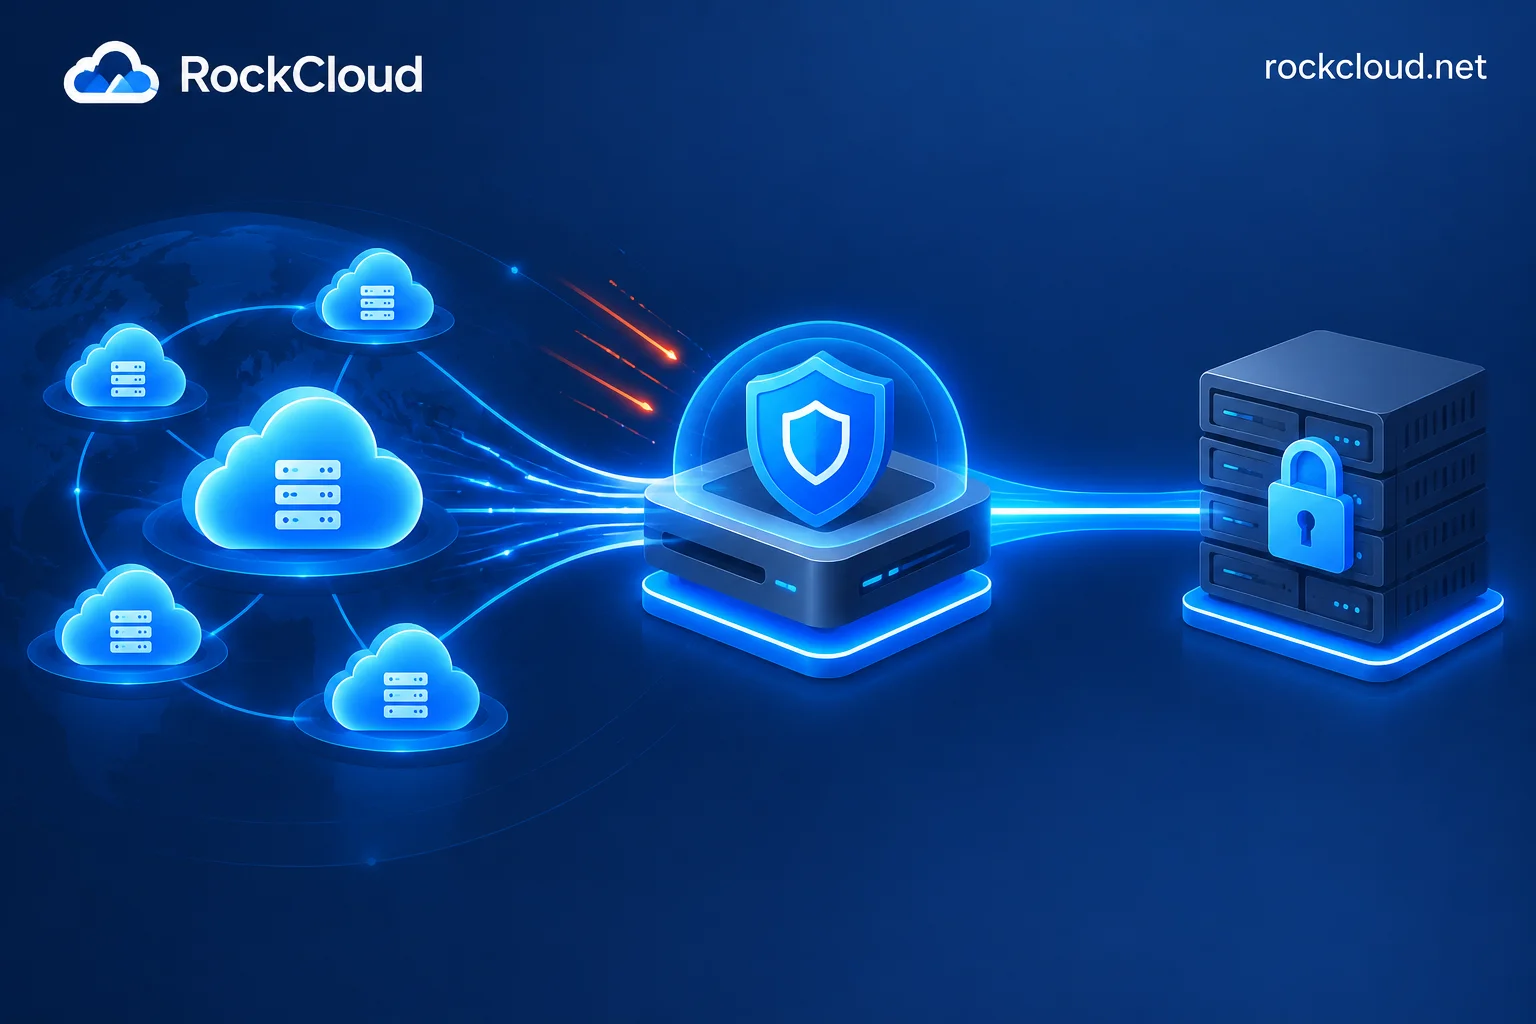
Can Anti-DDoS IP and Anti-DDoS CDN Be Used Together: Two Combined Architectures, Configuration Essentials, and Selection Criteria
Anti-DDoS IP and Anti-DDoS CDN can be used together, typically in a chained defense-in-depth setup or protocol-based traffic splitting. This article explains which business types suit each architecture, how to configure whitelists and real IP passthrough in a chain, how much complexity, latency, troubleshooting, and cost are added by stacking both layers, and when a single integrated solution is sufficient for ordinary web businesses.
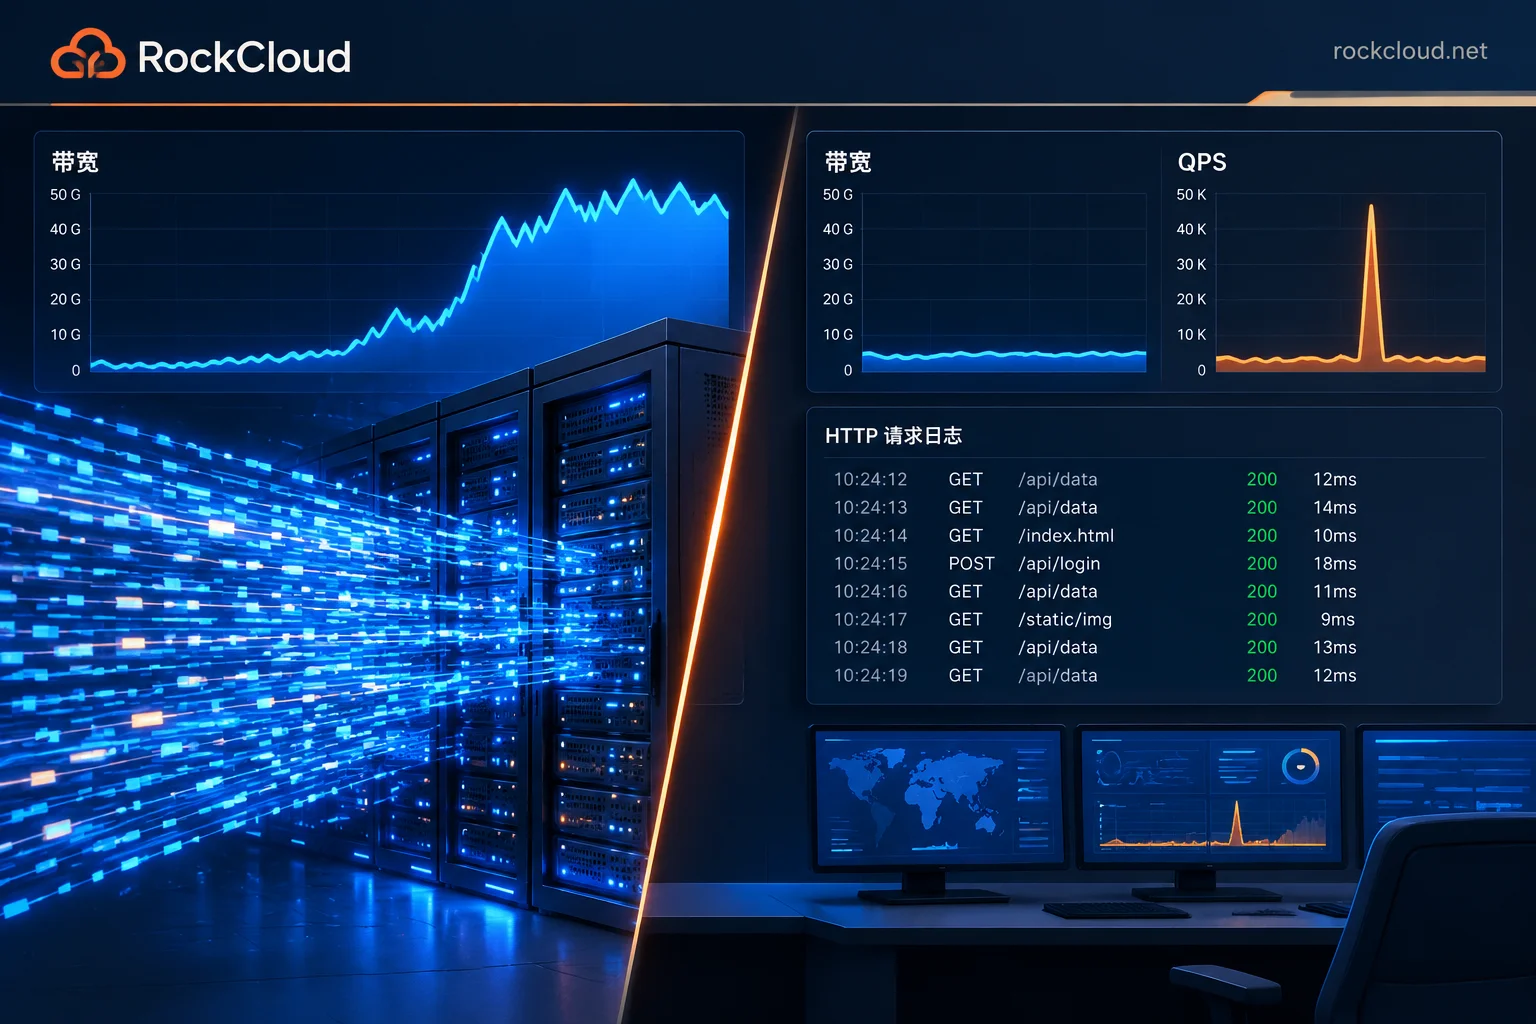
How to Tell If Your Website Is Under DDoS or CC Attack: Four-Step Diagnosis and Response
When a website suddenly goes down, three things can roughly distinguish the cause: whether bandwidth and packet volume spike, whether you can still log in to the server, and whether access logs show a flood of requests.
How to Choose Between Cloud WAF and Hardware WAF: Use Cases, Pros and Cons, and Selection Criteria
Compare cloud WAF and hardware WAF across five aspects: deployment, DDoS/CC capacity, operations, cost structure, and compliance controls. The article explains which business scenarios each suits, issues to watch in hybrid deployments, and conditions to verify before purchasing, helping website, gaming, API, and payment business owners decide which to choose.
Which Businesses Are Suited for Hong Kong CN2 DDoS-Protected Servers: Three Scenarios, Two Limitations, and Common Architectures
Hong Kong CN2 DDoS-protected servers are best for businesses that meet three conditions: primary users in mainland China, sensitivity to latency and packet loss, and frequent DDoS or CC attacks. This article explains the selection priorities for gaming, financial and payment APIs, and overseas-facing independent websites, analyzes two limitations—high bandwidth costs and route switching after attacks exceed capacity—and provides three architectures: standalone, front-end DDoS-protected CDN, and game shield, along with questions to confirm before procurement.