RockCloud-基石云安全-官方博客
RockCloud Blog
Insights on cloud security, DDoS protection, CDN acceleration and reliable infrastructure.
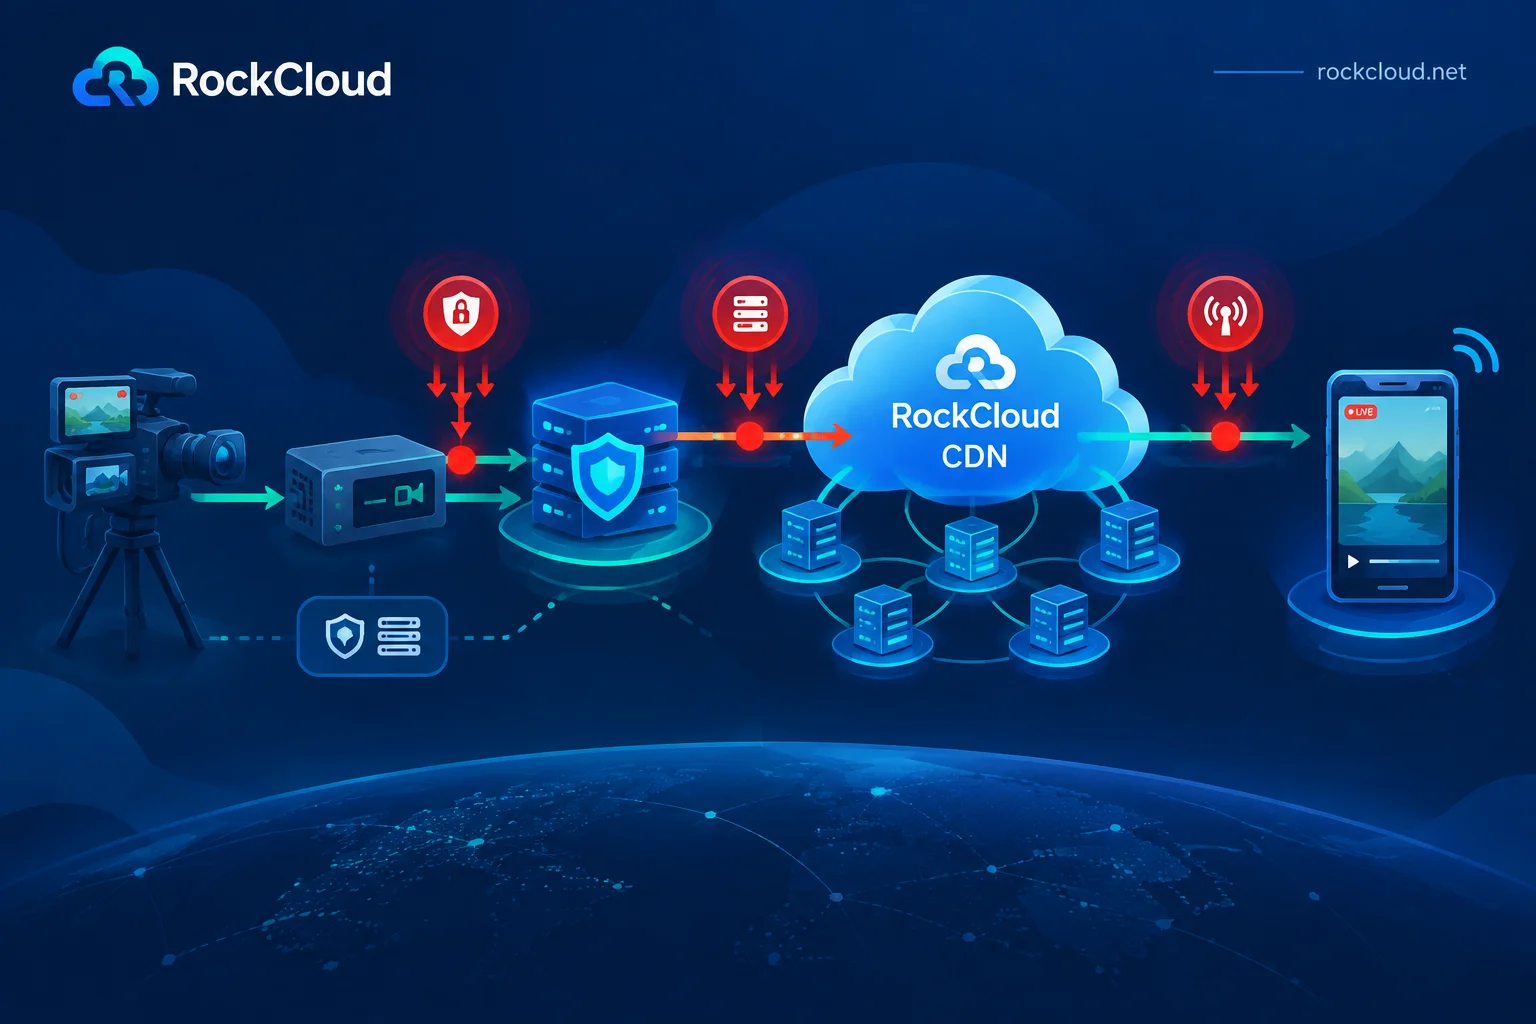
How to Handle Live Streaming Push Stream Lag from CC Attacks: Locate the Damaged Layer First, Then Stop the Bleeding in Order
When live streaming lags or frequently disconnects, spend the first ten minutes determining whether the signaling/auth API is being flooded, the playback side is penetrating back to the origin and saturating it, or the push port is being exhausted by empty connections, then apply rate limiting, cache convergence, and port closure at the corresponding layer.
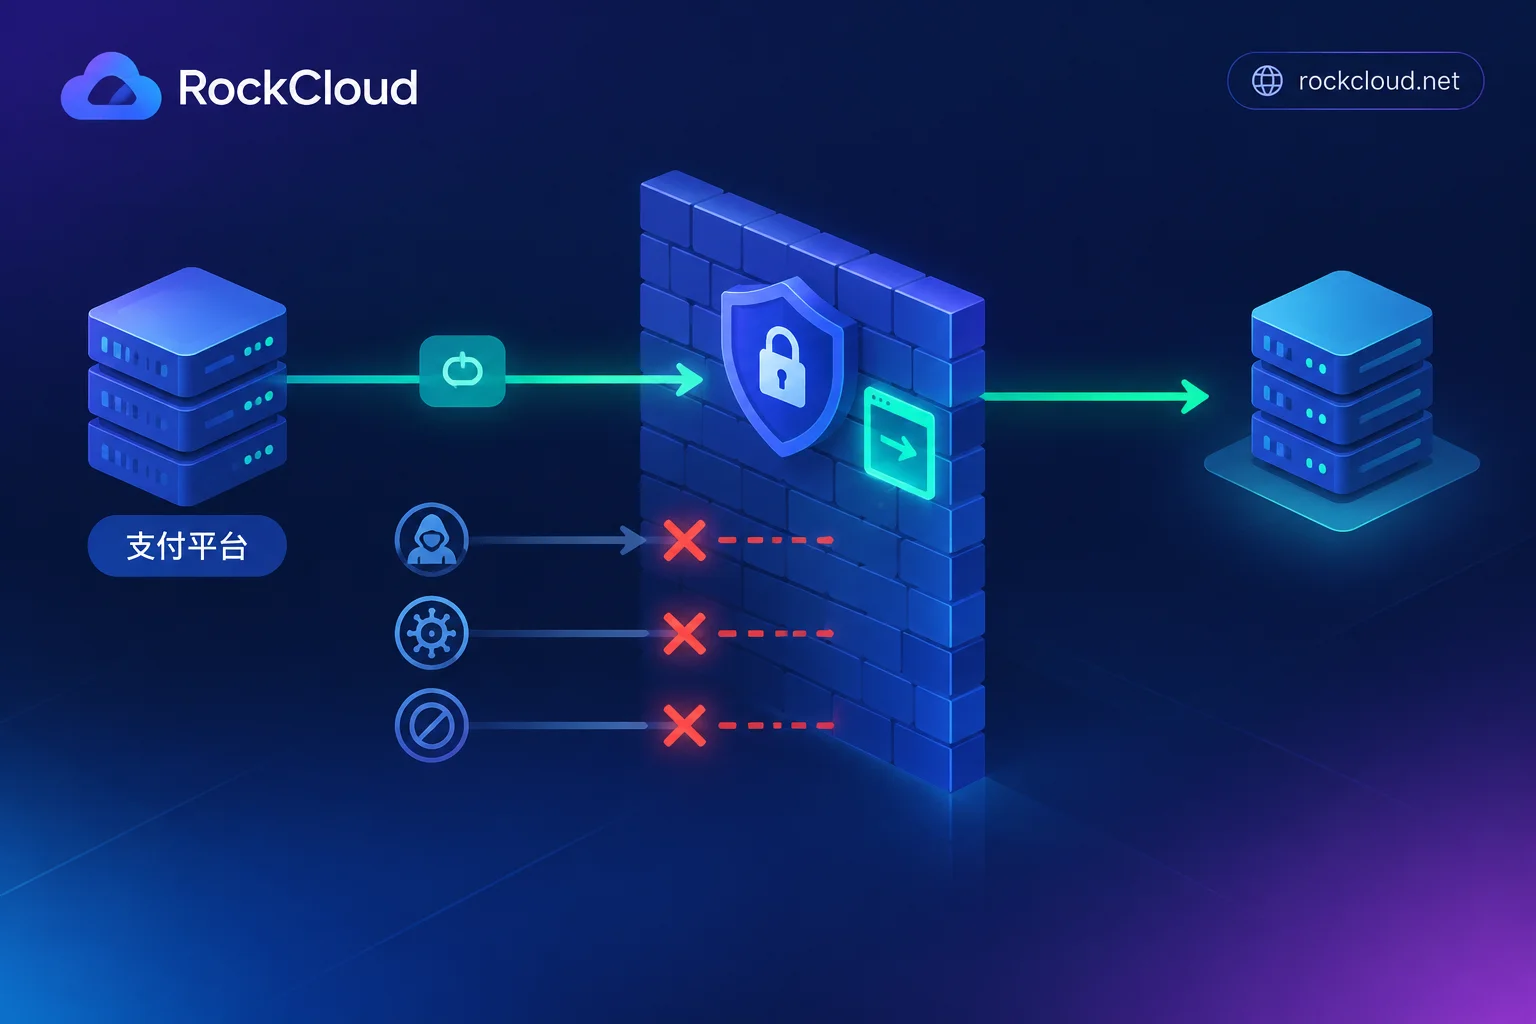
WAF Blocked Your Payment Callback? How to Whitelist: Check Rule ID First, Then Add IP Precise Allow by Path
Payment succeeds but orders don't update, and the payment platform reports notification failure—most likely the WAF treated the callback request as an attack. This article provides the recovery order: first locate the blocking module and rule ID in the interception logs, then use a combination of 'POST + callback path + payment platform official IP range' to allow only that endpoint and only skip the hit module, finally resend the notification to verify, and retain business-layer signature verification.
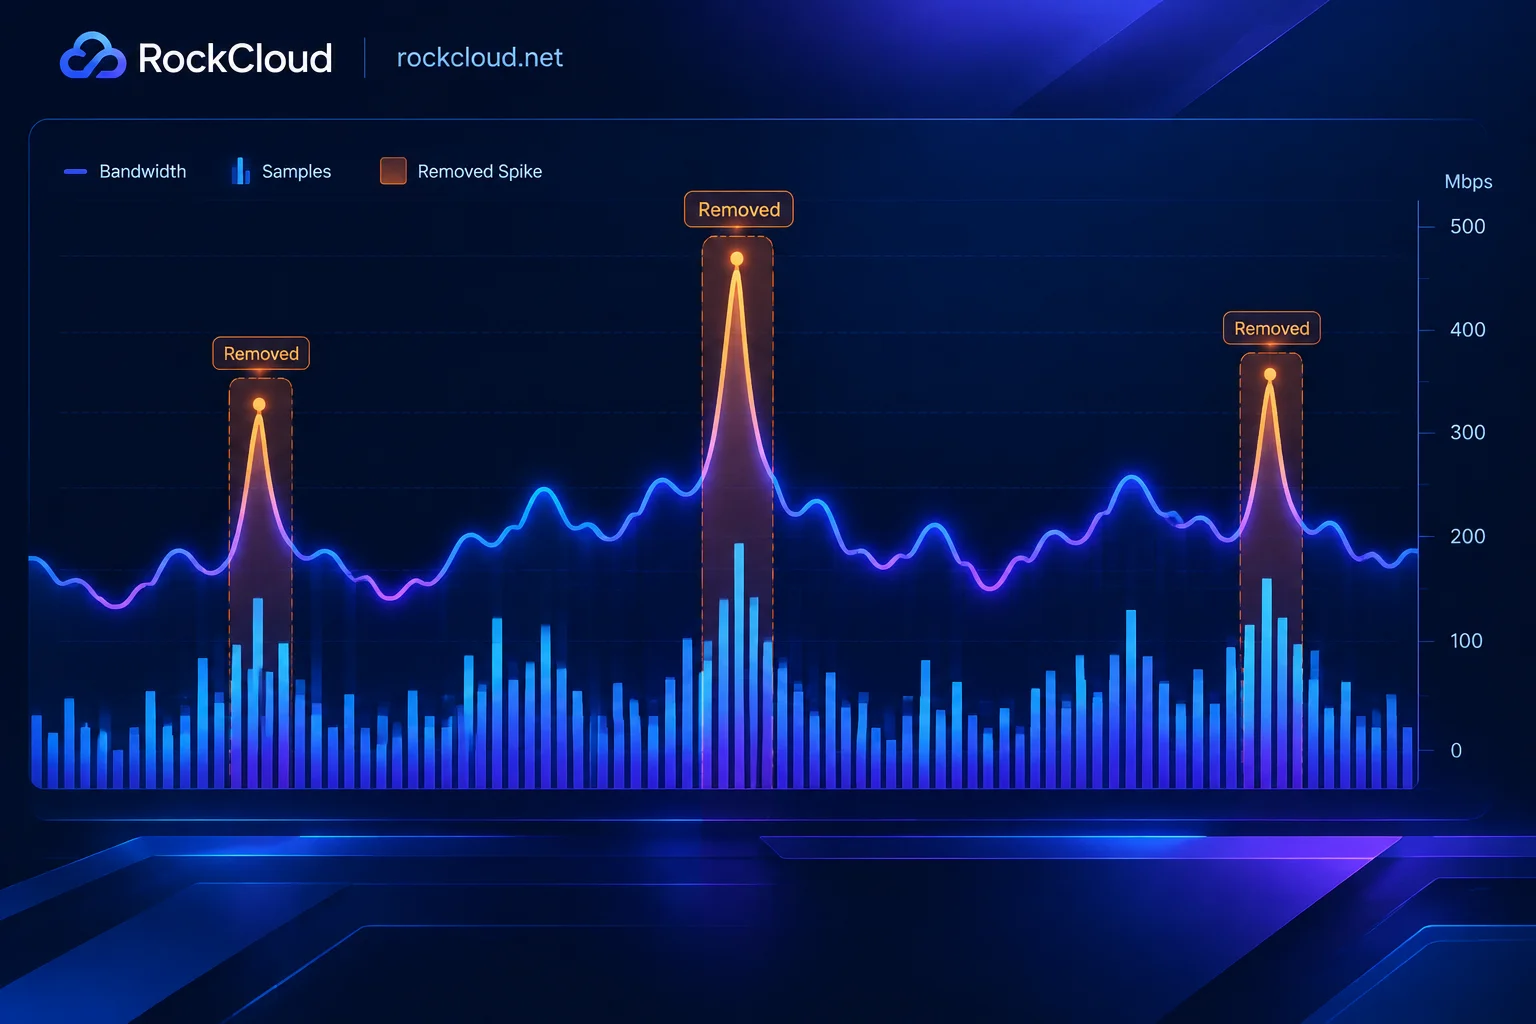
How Peak-Based Billing Works for High-Defense CDN: Three Algorithms from 5-Minute Sampling Points to Monthly 95th and Fixed Peak
Peak-based billing measures bandwidth, not traffic volume. This article explains how 5-minute sampling points are generated, the formulas and differences of four algorithms (daily peak, monthly 95th percentile, daily peak averaged monthly, and fixed peak monthly subscription), how to back-calculate the Mbps you need from existing traffic, and the overage handling, statistical scope, and protocol overhead issues you must clarify before signing a contract.
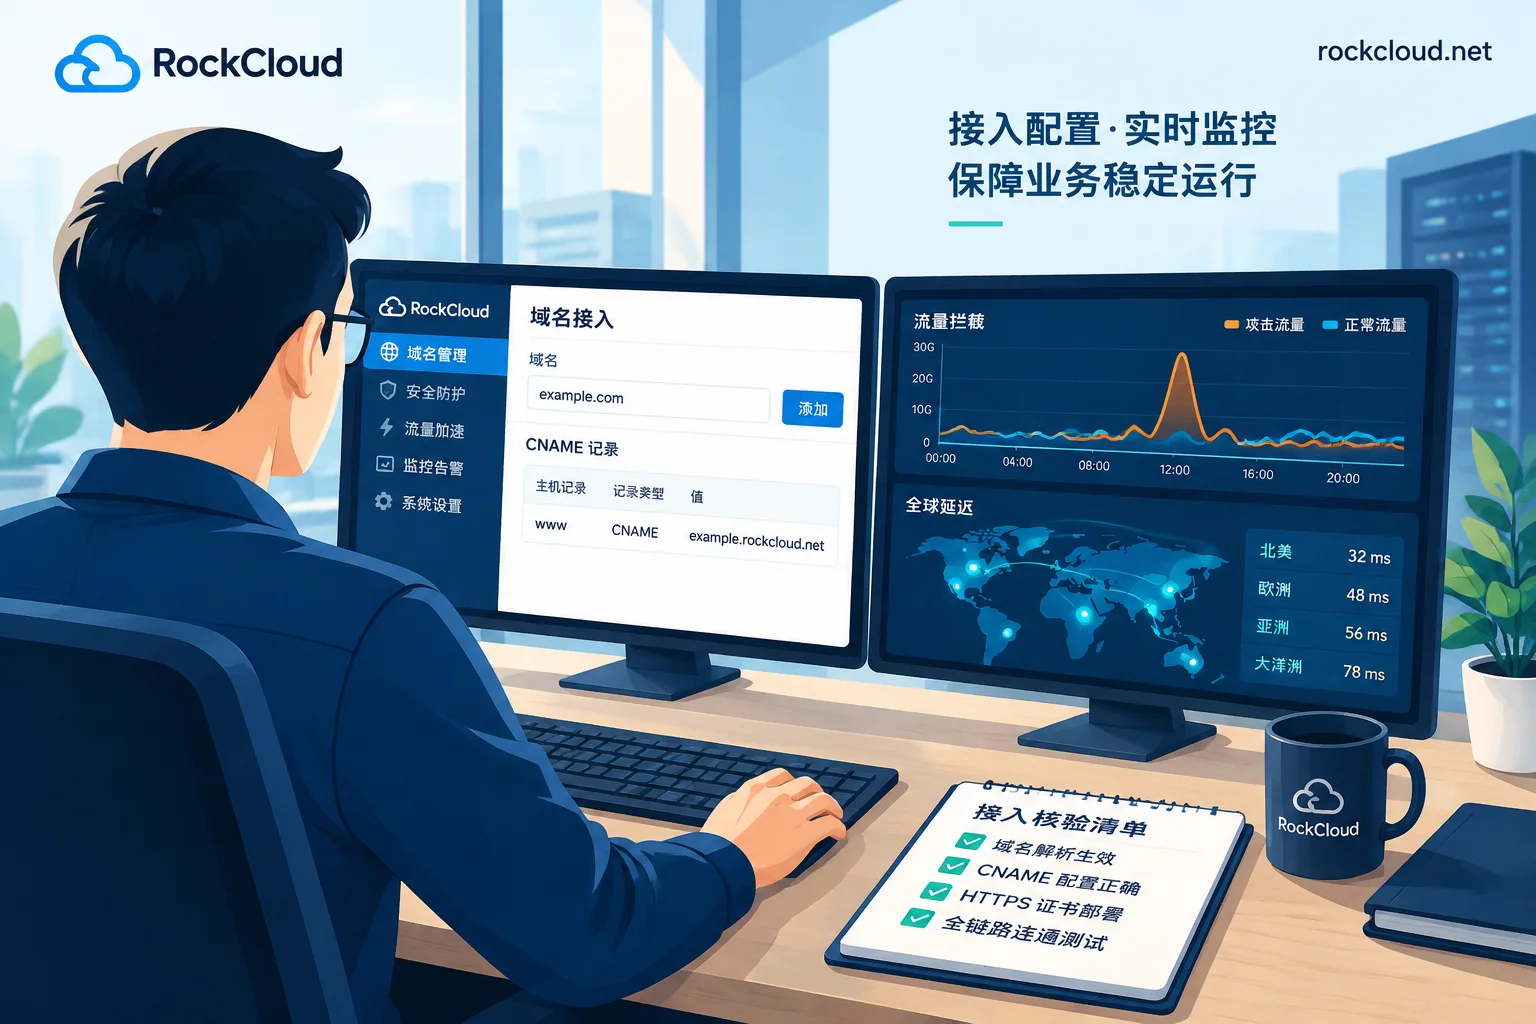
How to Apply for a Free Trial of a High-Defense CDN: Materials, Onboarding Sequence, and Verification Points During the Trial Period
Applying for a free trial of a high-defense CDN: the real work lies in clearly describing your business, onboarding in the correct sequence, and verifying the right metrics during the trial window.
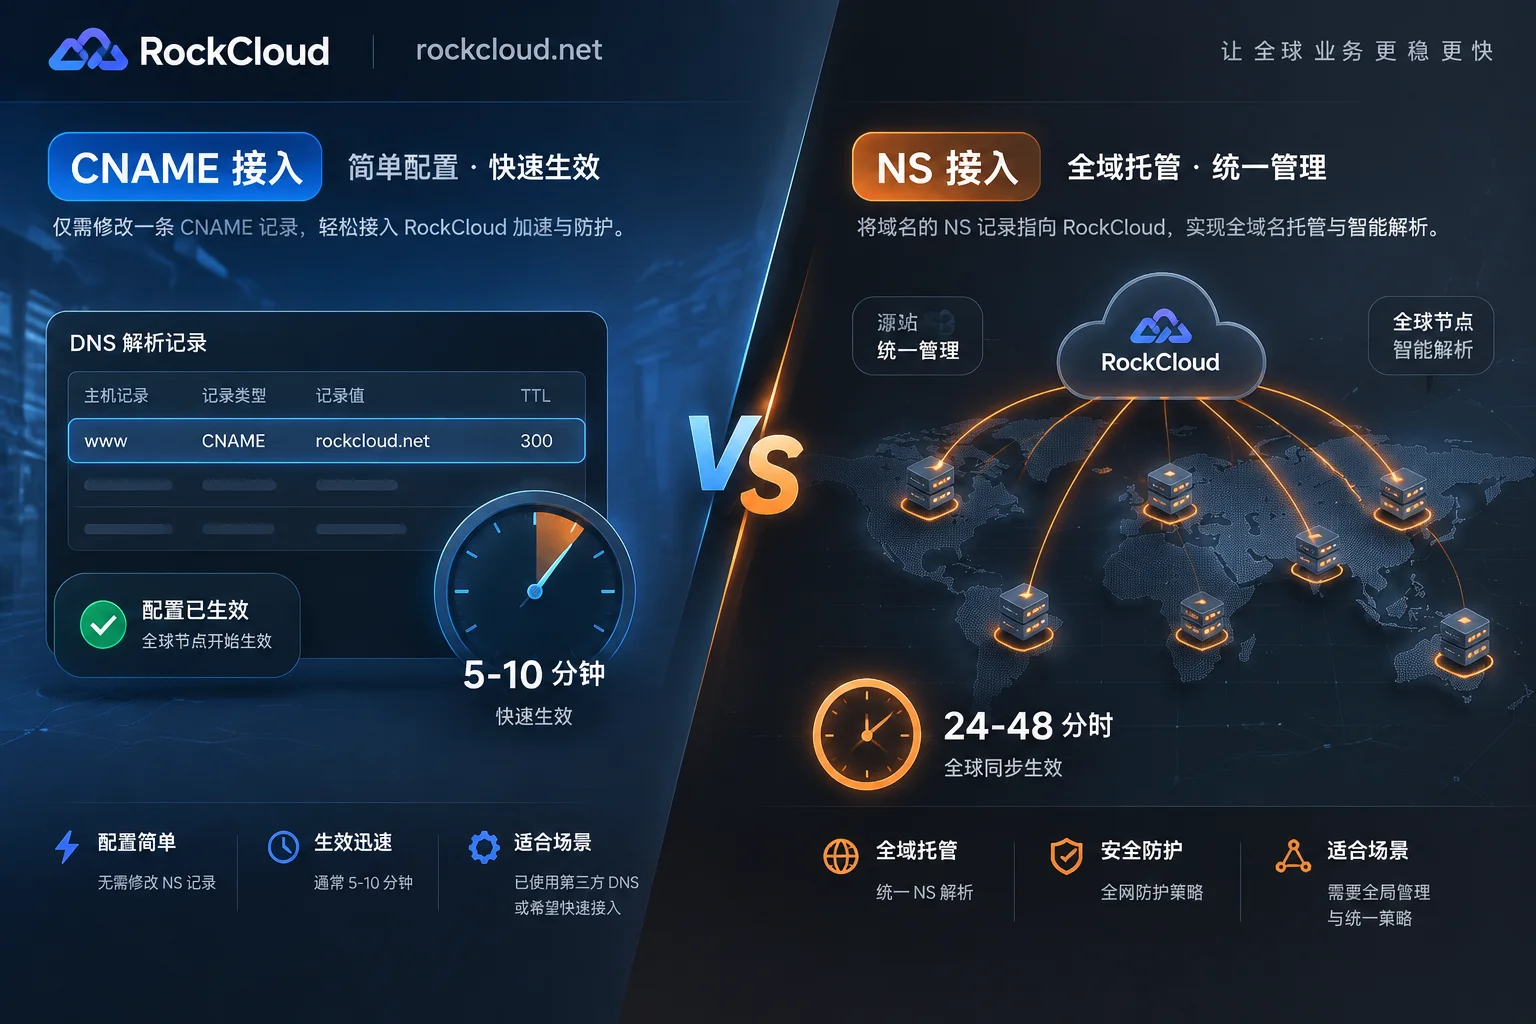
Does High-Defense CDN Require Changing NS: CNAME vs NS Activation Speed, Protection Boundaries, and Selection Criteria
High-defense CDN access does not require changing NS records; CNAME access takes effect in minutes with limited protection scope, while NS access offers full-domain protection including DNS layer but requires hours to 48 hours to propagate globally.