RockCloud-基石云安全-官方博客
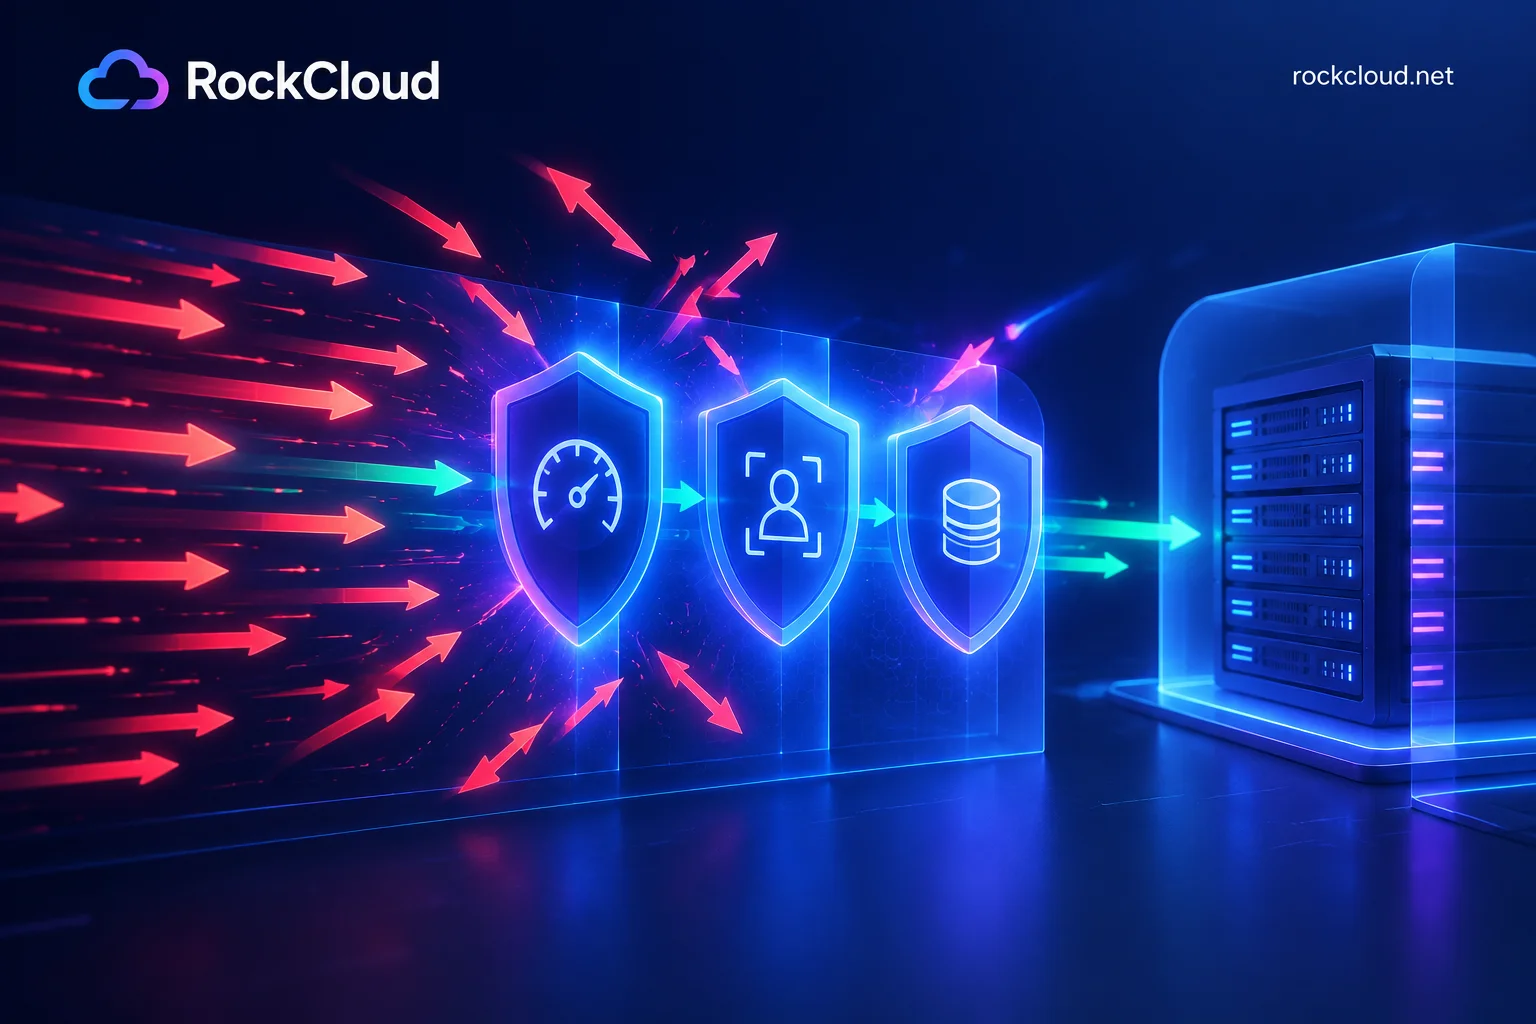
Can High-Defense CDN Stop CC Attacks? How It Blocks, When It Fails, and Post-Setup Checks
High-defense CDN can stop CC attacks, but two conditions must be met: edge nodes must have Layer 7 scrubbing capabilities, and the origin must only be accessible via the CDN. This article explains the four methods high-defense CDN uses to block CC attacks, lists four common failure scenarios—origin IP exposure, dynamic interface penetration, challenge misfires, and non-HTTP traffic—and provides a post-setup self-check sequence and key questions to ask when choosing a provider.
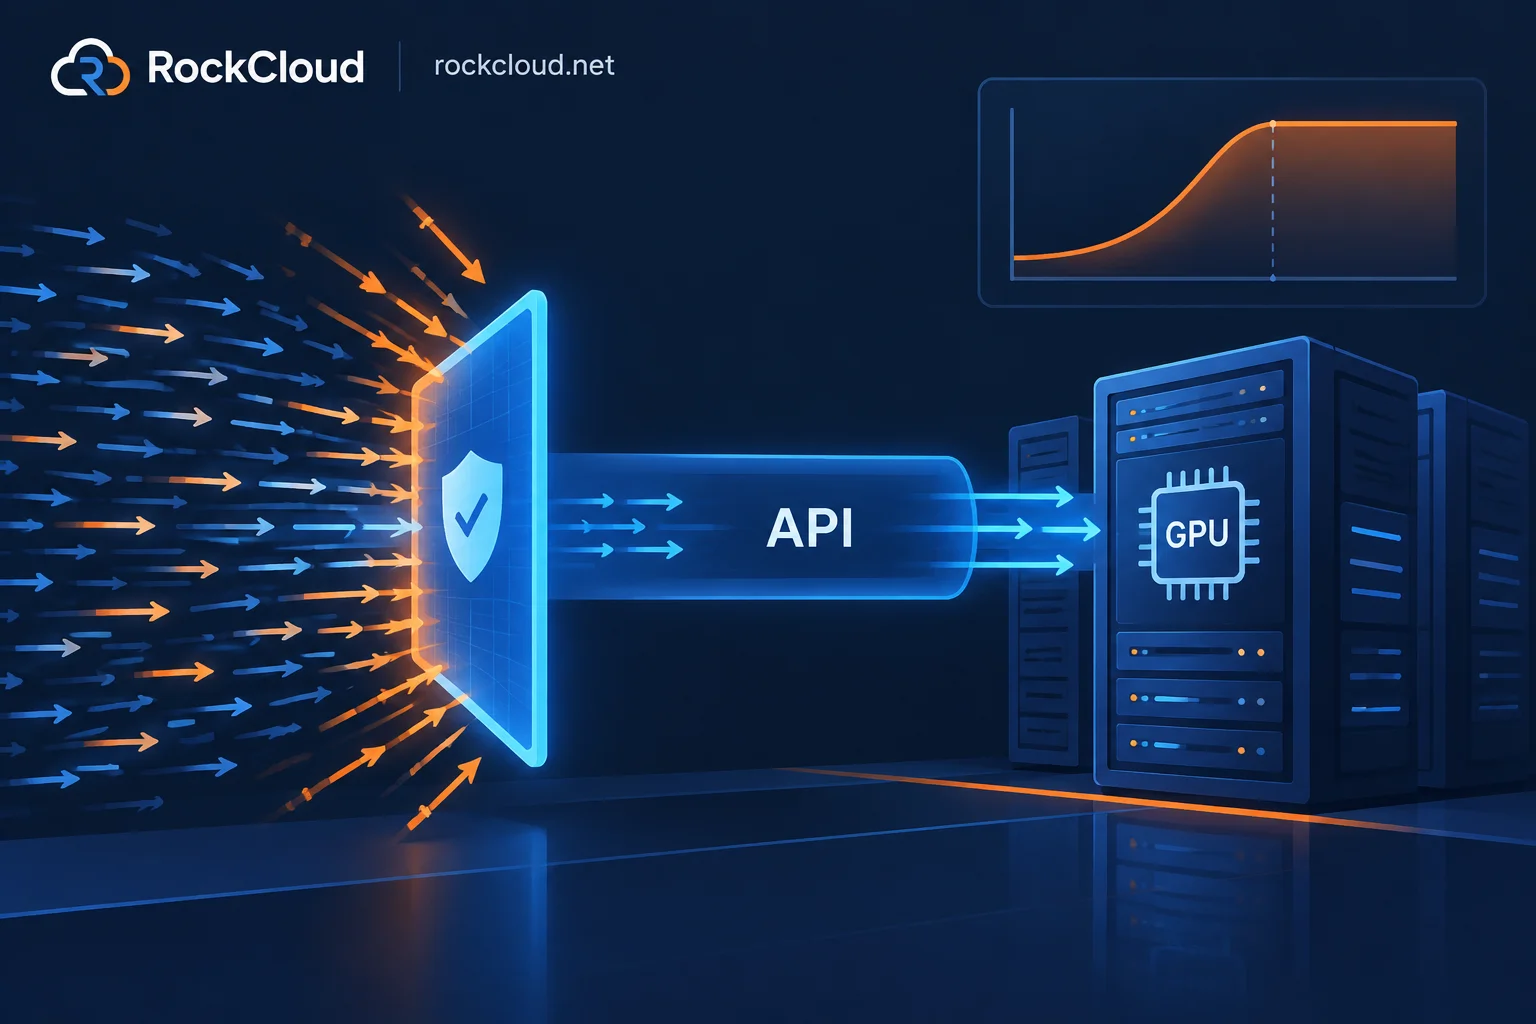
How to Rate-Limit Stolen Large-Model API Calls: Stop the Bleeding First, Then Set Tiered Thresholds by Token
When large-model APIs are abused, IP-based RPS limits often fail because cost lies in tokens and inference time; this article gives the first-hour containment sequence and explains the four dimensions rate limiting must cover, plus gateway composite-key configurations.
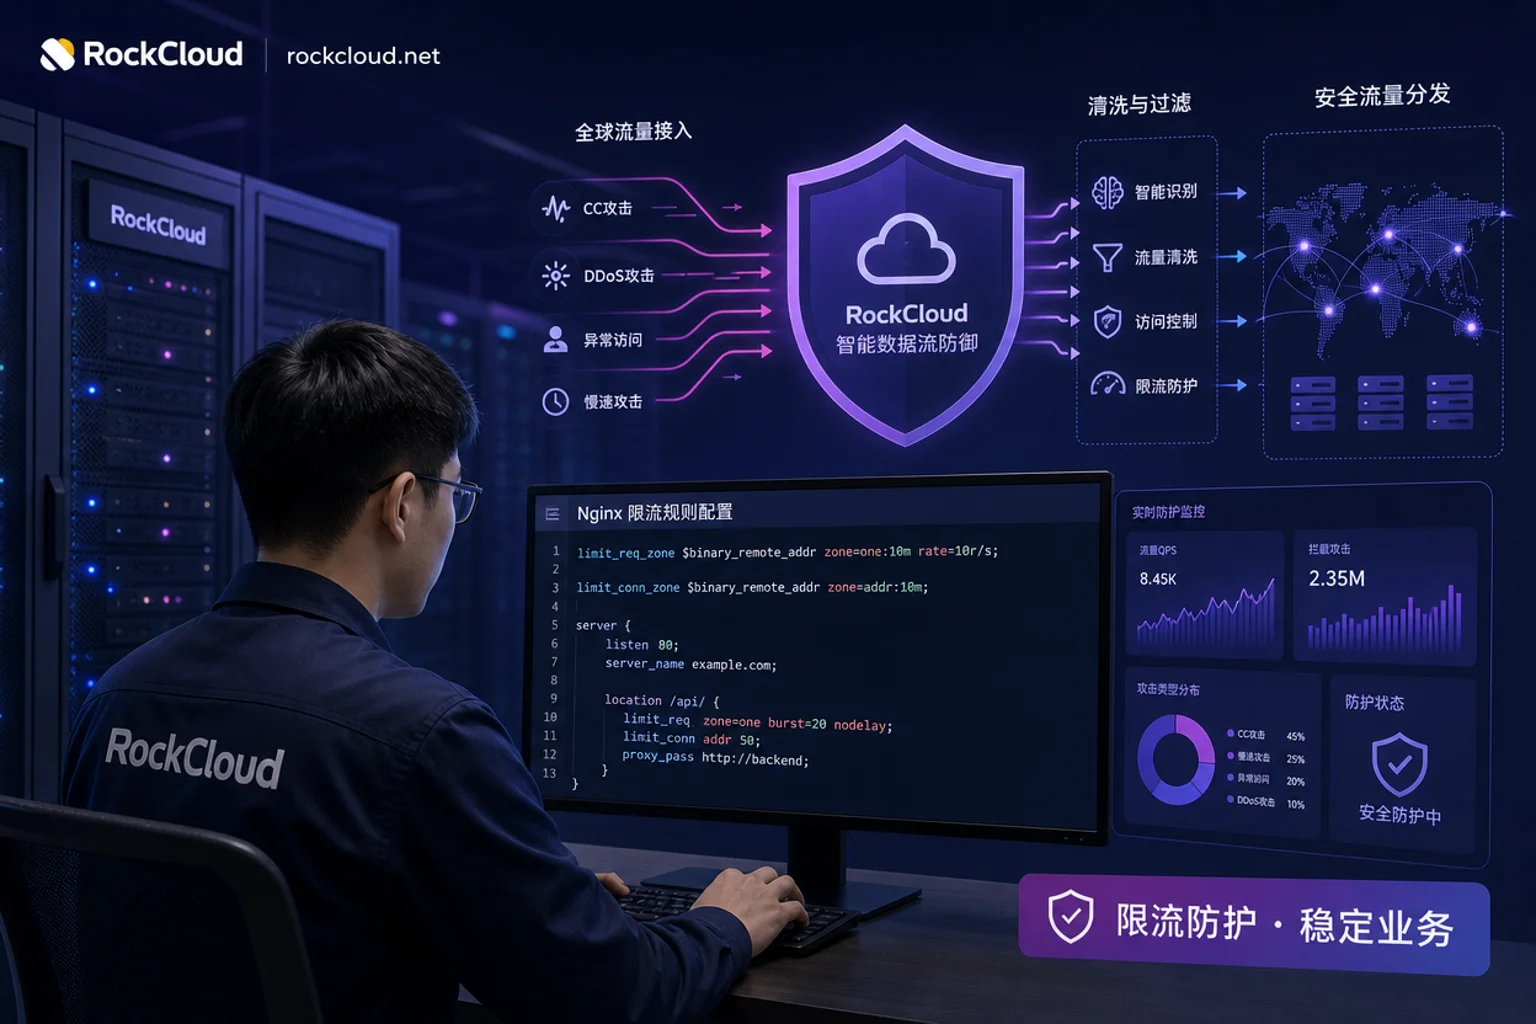
Nginx Anti-CC Attack Rate Limiting Best Practices: Should You Limit Connections or Requests First?
Discover the best practices for configuring Nginx to defend against CC attacks, combining connection limits, request rate limiting, burst handling, and whitelist exemptions.
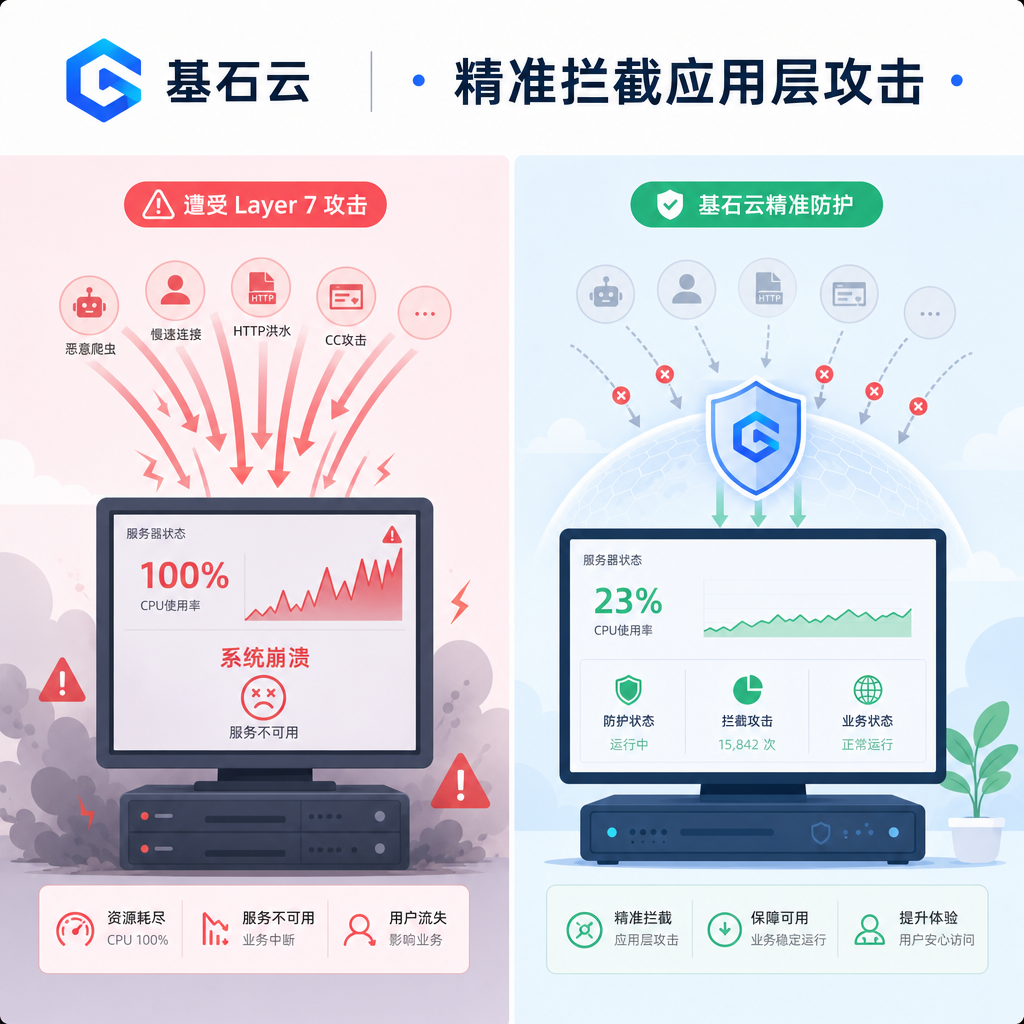
Application-Layer Attacks Double in Two Years: Why Do Conventional CC Defense Configurations Keep Failing?
As application-layer attacks surge 104% in two years, traditional CC defenses relying on bandwidth monitoring fail against low-volume, high-cost requests that exhaust server CPU and memory.