RockCloud-基石云安全-官方博客
RockCloud Blog
Insights on cloud security, DDoS protection, CDN acceleration and reliable infrastructure.
How Much Traffic Can BGP High-Defense Mitigate: What Determines the Limit, What Happens When Exceeded, and How Much to Buy
The mitigation capacity of BGP high-defense has no universal number: a single node typically handles tens to hundreds of Gbps, while Anycast distributed architectures can reach several Tbps across the network. What truly determines how much you can withstand are node bandwidth, scrubbing device processing power, and the committed and elastic specifications in your contract; exceeding the limit results in IP blackholing. This article provides steps to estimate mitigation specifications and questions to ask during procurement.
Why Single-Line High-Defense Is Much Cheaper: What You Save on Multi-Line Bandwidth and Cross-Network Redundancy, and Who Pays the Price
Single-line high-defense is cheap mainly because it buys bandwidth from one carrier and skips BGP multi-line routing and redundancy; the savings become cross-network latency for off-network users, who may even be unable to connect during attacks.
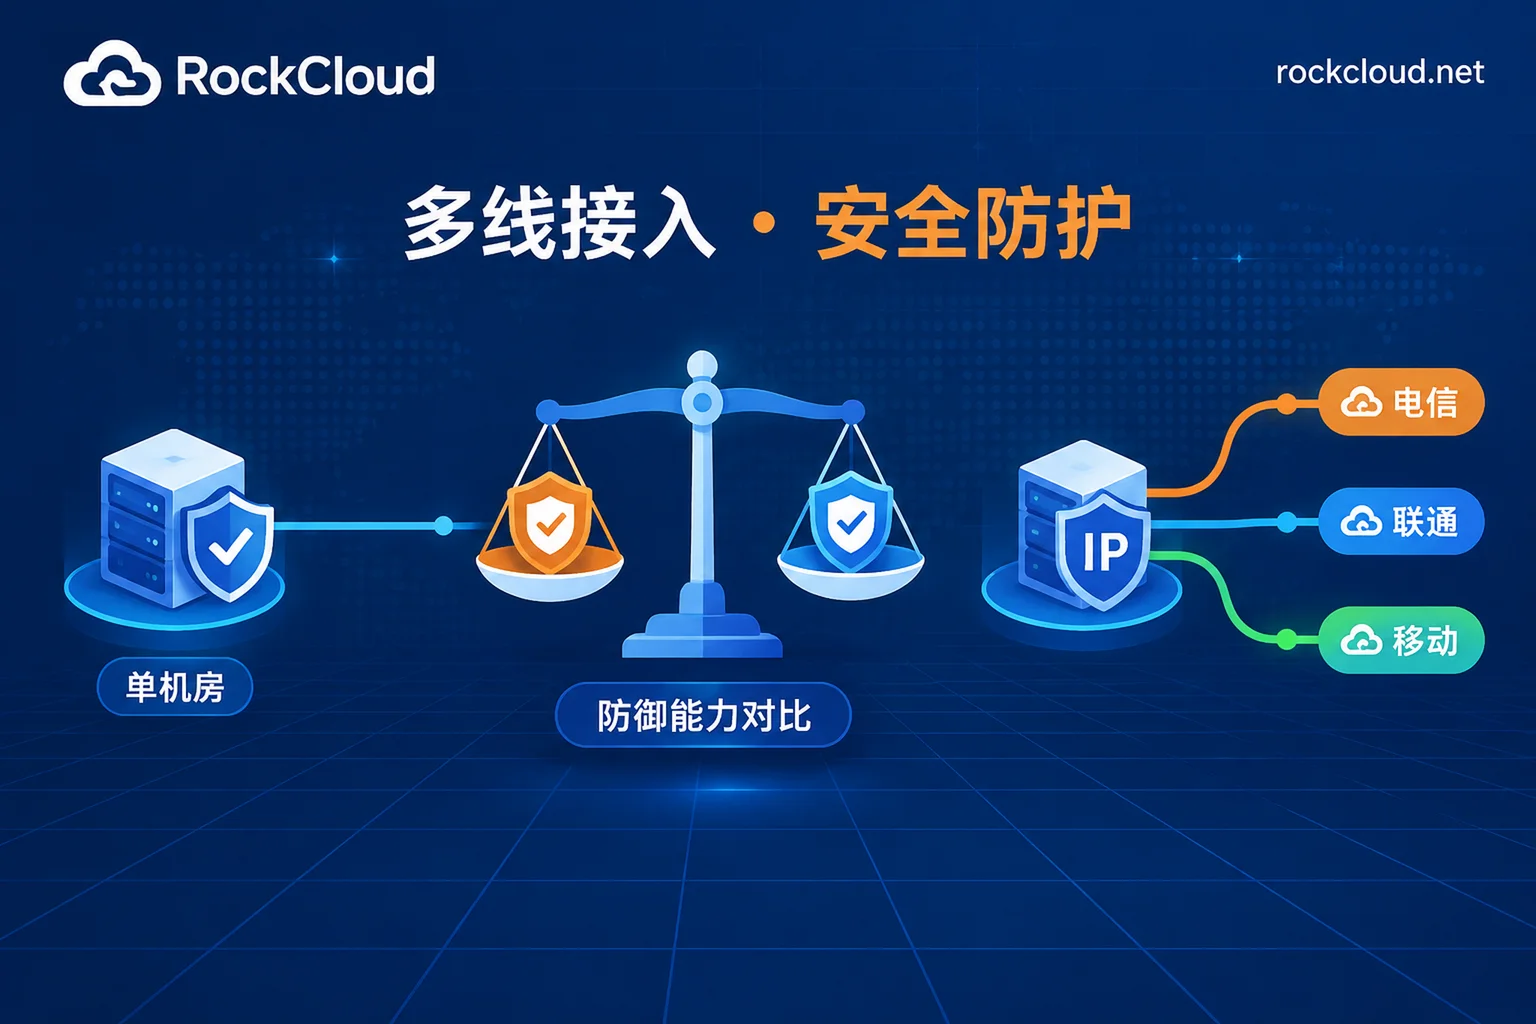
BGP High-Defense vs Single-Line High-Defense: Which Is Stronger — Look at Scrubbing Capacity and Whether Users Can Still Access During an Attack
Paper defense peaks are often higher and cheaper on single-line high-defense, but when users are spread across different carriers, BGP high-defense better preserves nationwide access during an attack. This article breaks down "defense capability" into three criteria, gives business-based selection conclusions, and lists what to ask and test during procurement and testing.
What to Do When a Hong Kong CN2 Server Is Hit by DDoS: Confirm Blackhole, Switch IP, Add Protection, Then Lock Down the Origin
Recovery sequence after a Hong Kong CN2 server is knocked offline by DDoS: check if it's in blackhole, decide whether to wait or change IP, add high-defense based on protocol, allow only origin-pull subnets at the origin, and finally audit IP leaks.
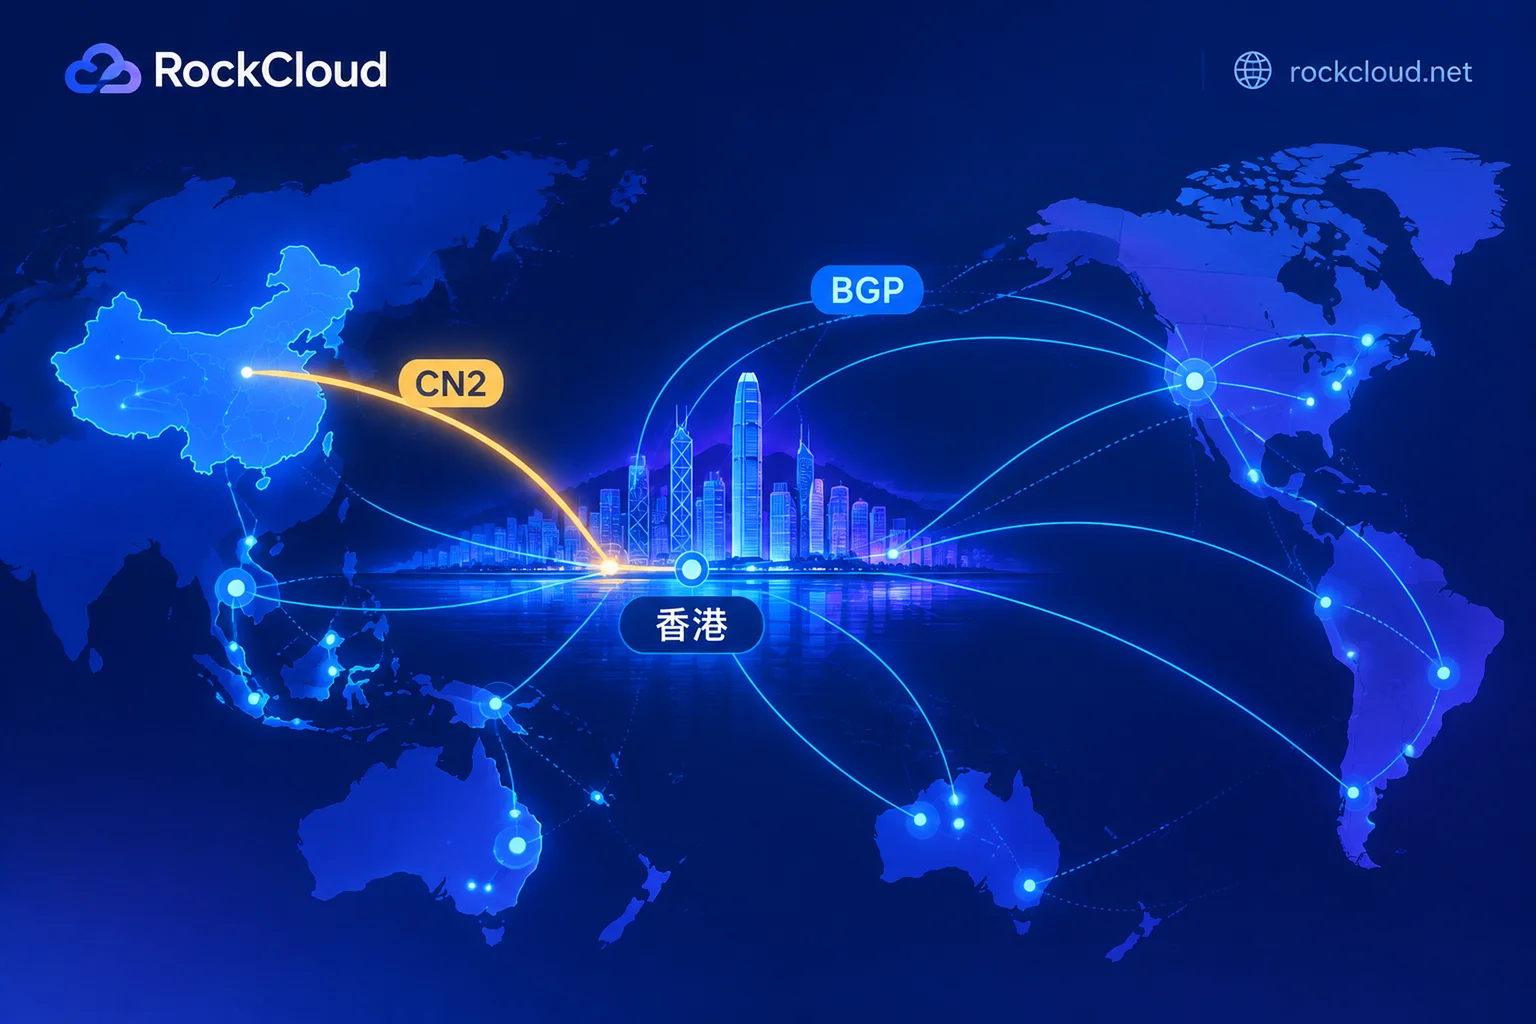
Hong Kong CN2 vs Hong Kong BGP: Which Is Better? It Depends on Your Users, Latency Needs, and Bandwidth Budget
Hong Kong CN2 and Hong Kong BGP are not the same layer of concept. This article first clarifies the difference, then explains their gaps in mainland peak hours, overseas coverage, and bandwidth cost, and provides selection criteria by business type plus pre-purchase verification items.