RockCloud-基石云安全-官方博客
RockCloud Blog
Insights on cloud security, DDoS protection, CDN acceleration and reliable infrastructure.
Will the Origin IP Still Be Exposed After Enabling a High-Defense CDN? Five Leak Paths, Hardening Order, and Post-Exposure Response
Even after enabling a high-defense CDN, the origin IP can still leak via historical DNS records, subdomains, email, certificate scans, and application outbound connections. This article provides self-check methods for each leak path, explains the hardening order such as origin whitelisting and default site blocking, and clarifies why you should plug the leaks first and then change the IP when the origin is under direct attack.
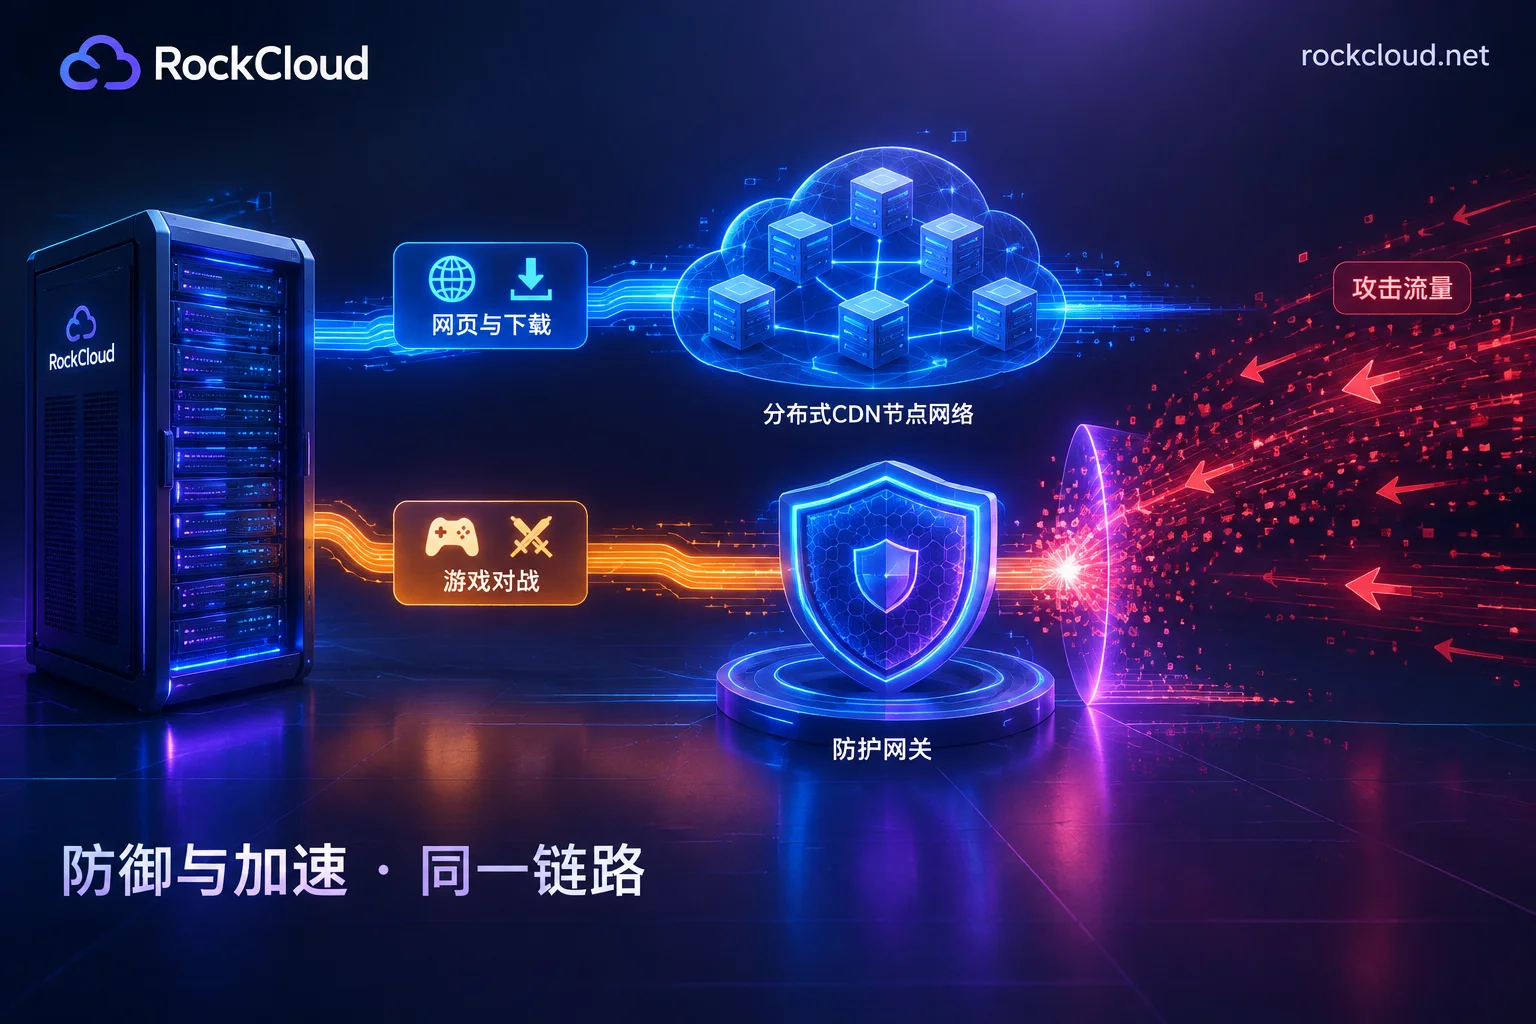
Game Servers: High-Defense IP or High-Defense CDN? Split Modules by Protocol and Layer Your Access
Most games don't need to choose between high-defense IP and high-defense CDN; this article splits game services by protocol into Web modules and real-time connection modules, explains which modules use high-defense CDN and which use high-defense IP or game shield, and provides key points for combined deployment and the access sequence when under attack.
Can High-Defense CDN Stop CC Attacks? How It Blocks, When It Fails, and Post-Setup Checks
High-defense CDN can stop CC attacks, but two conditions must be met: edge nodes must have Layer 7 scrubbing capabilities, and the origin must only be accessible via the CDN. This article explains the four methods high-defense CDN uses to block CC attacks, lists four common failure scenarios—origin IP exposure, dynamic interface penetration, challenge misfires, and non-HTTP traffic—and provides a post-setup self-check sequence and key questions to ask when choosing a provider.
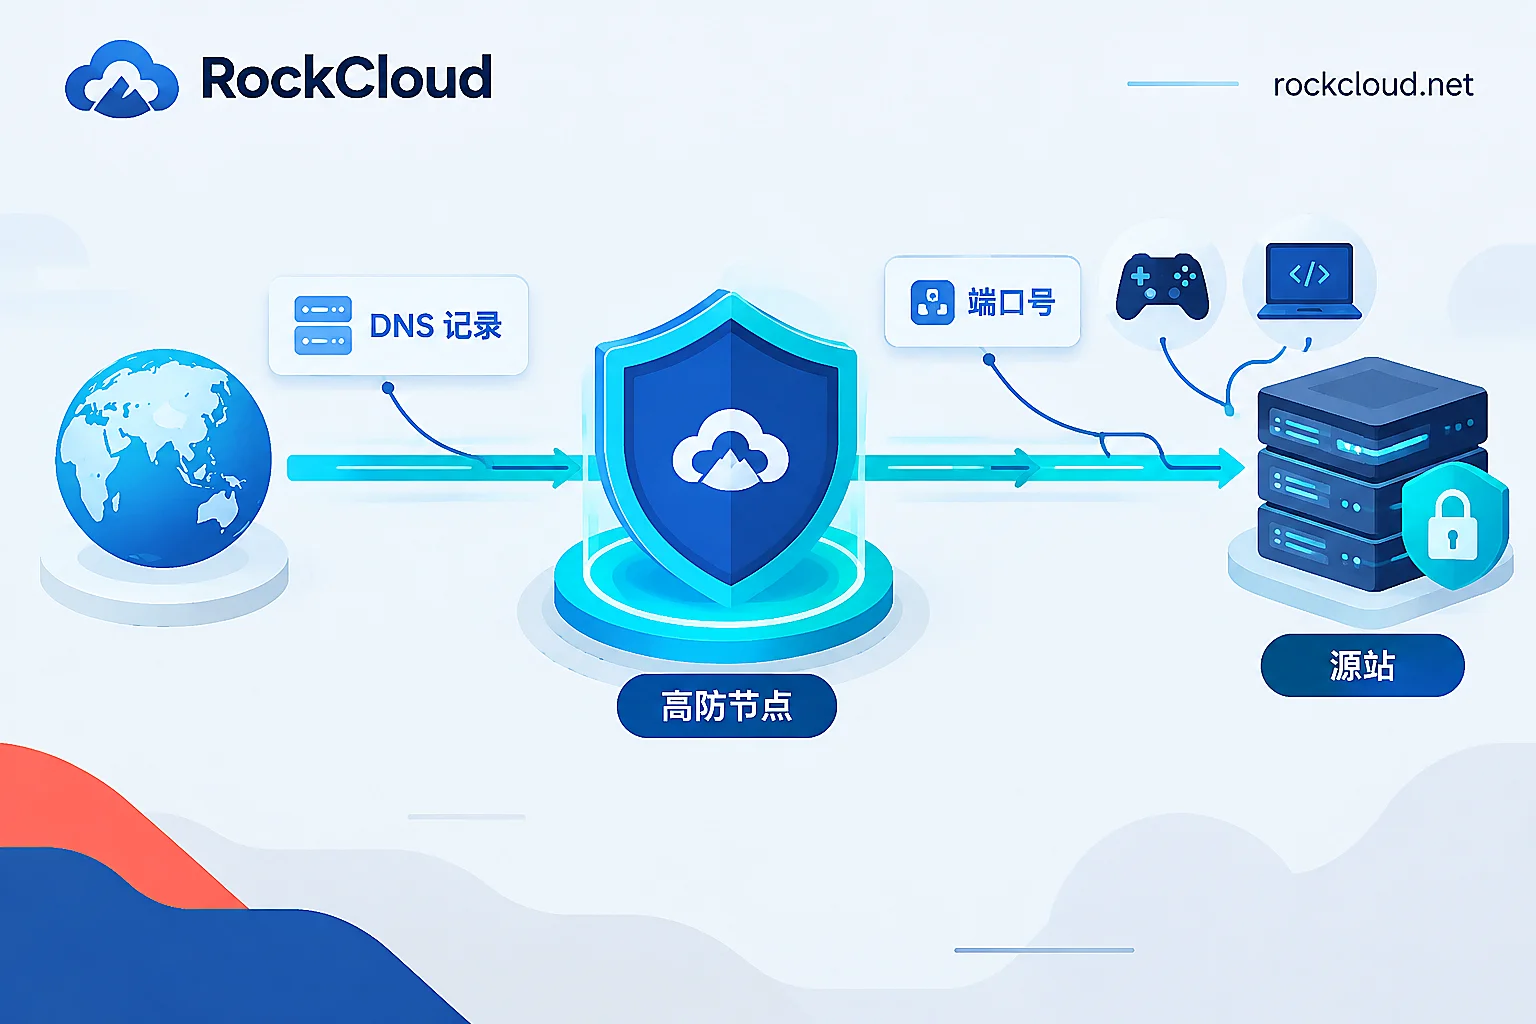
High-Defense IP: Change DNS or Change Ports? Understanding the Change Points and Onboarding Order by Business Type
When onboarding a high-defense IP, you usually change the user access entry point rather than the origin server's listening port: website businesses change DNS, while TCP/UDP businesses configure forwarding rules and then replace the client connection address.
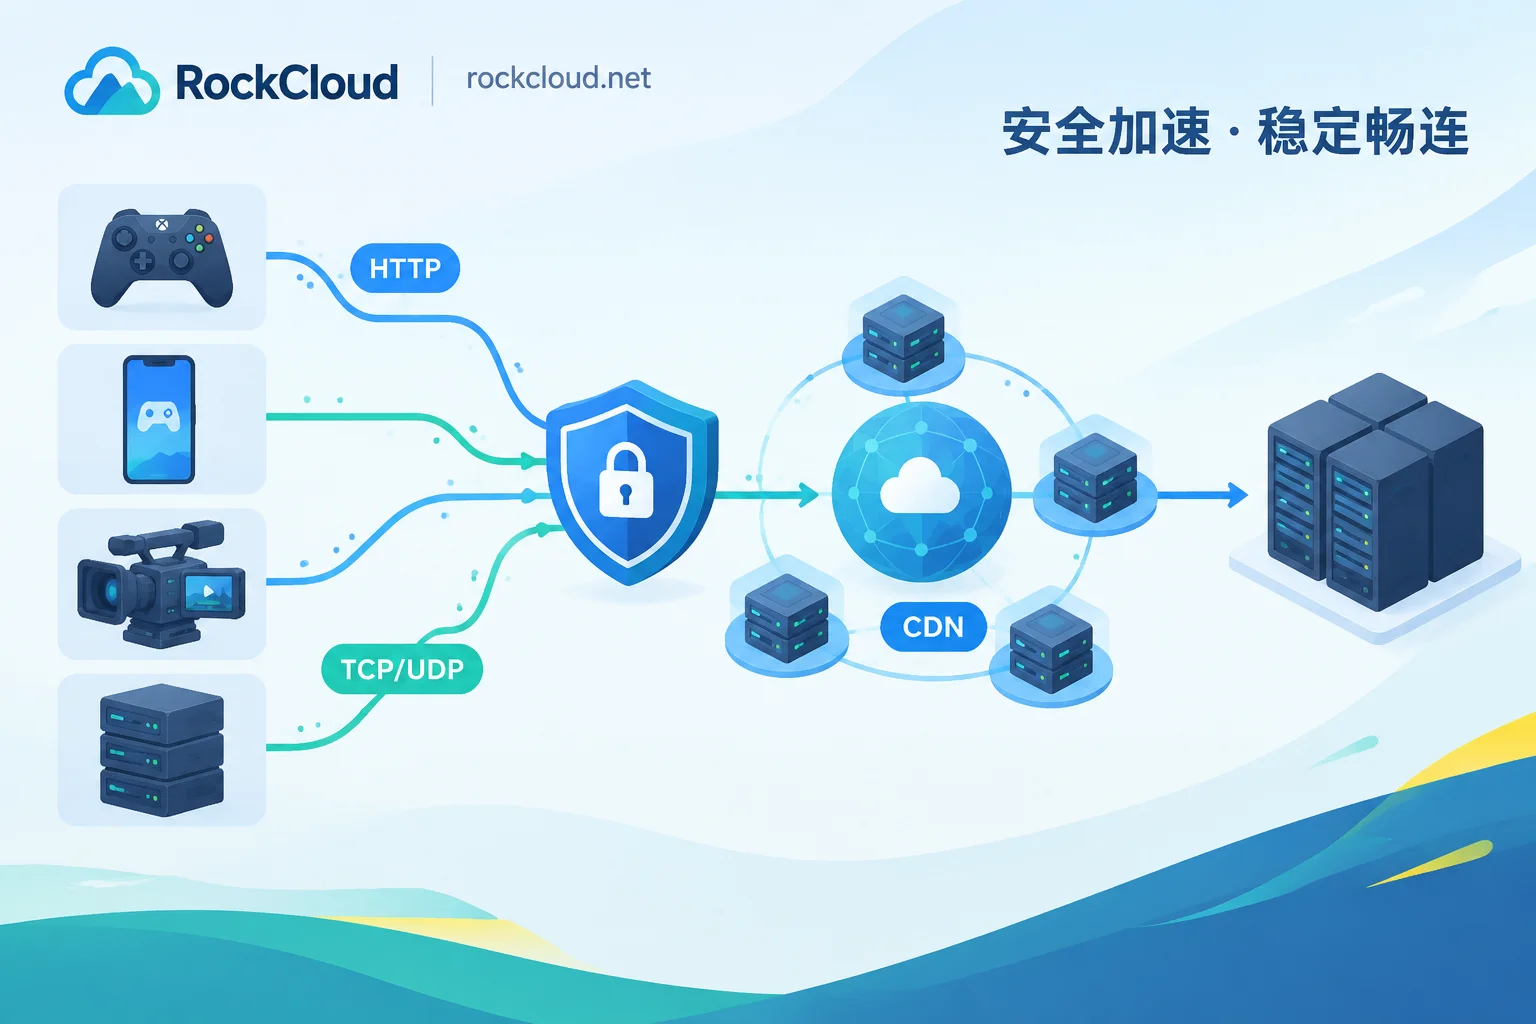
Can Non-Website Services Use Anti-DDoS CDN? Identify the Protocol First, Then Choose Anti-DDoS CDN, Layer 4 Proxy, or Game Shield
If your service uses HTTP/HTTPS, it can connect directly to an anti-DDoS CDN; if it uses raw TCP/UDP or a private protocol, traditional anti-DDoS CDNs cannot handle it, and you need a Layer 4 proxy, anti-DDoS IP, or game shield instead. This article selects solutions based on four criteria: protocol, client, port, and origin hiding requirements, and lists pre-integration checks for real IP, origin exposure, and hybrid service splitting.