RockCloud-基石云安全-官方博客
只是一个默认分类
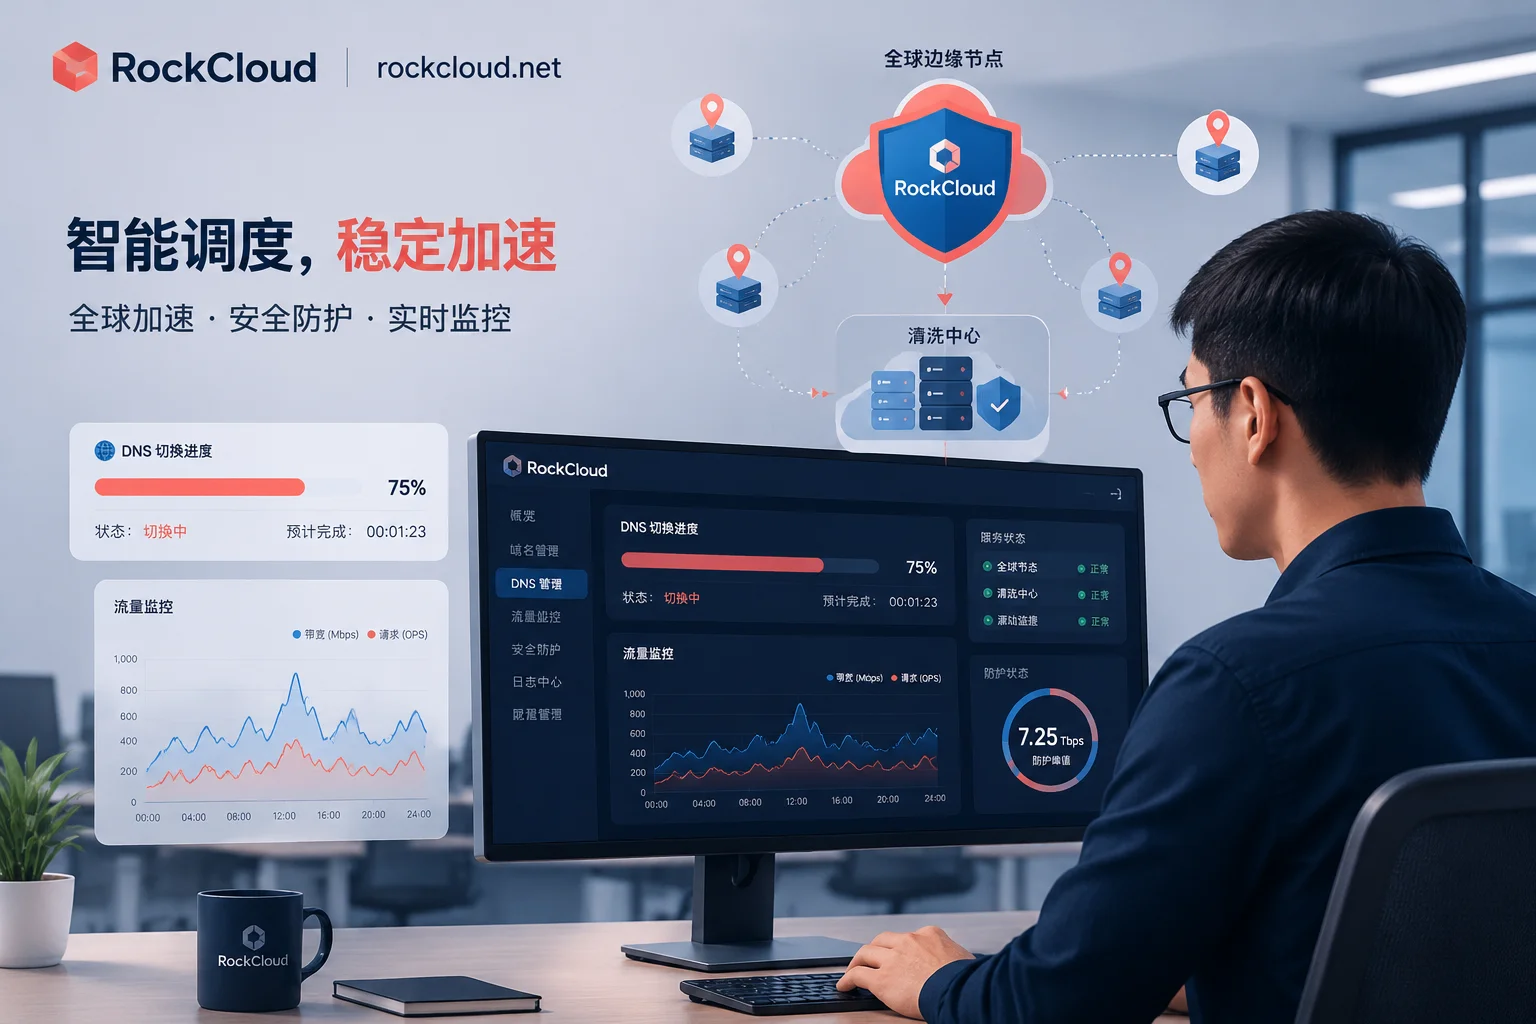
Seamless High-Defense CDN Onboarding: 6 Steps for Zero-Downtime Migration
Follow this 6-step process to integrate a high-defense CDN without downtime, covering DNS TTL reduction, origin pre-whitelisting, certificate alignment, gray traffic shifting, real IP passthrough, and origin whitelist lockdown.
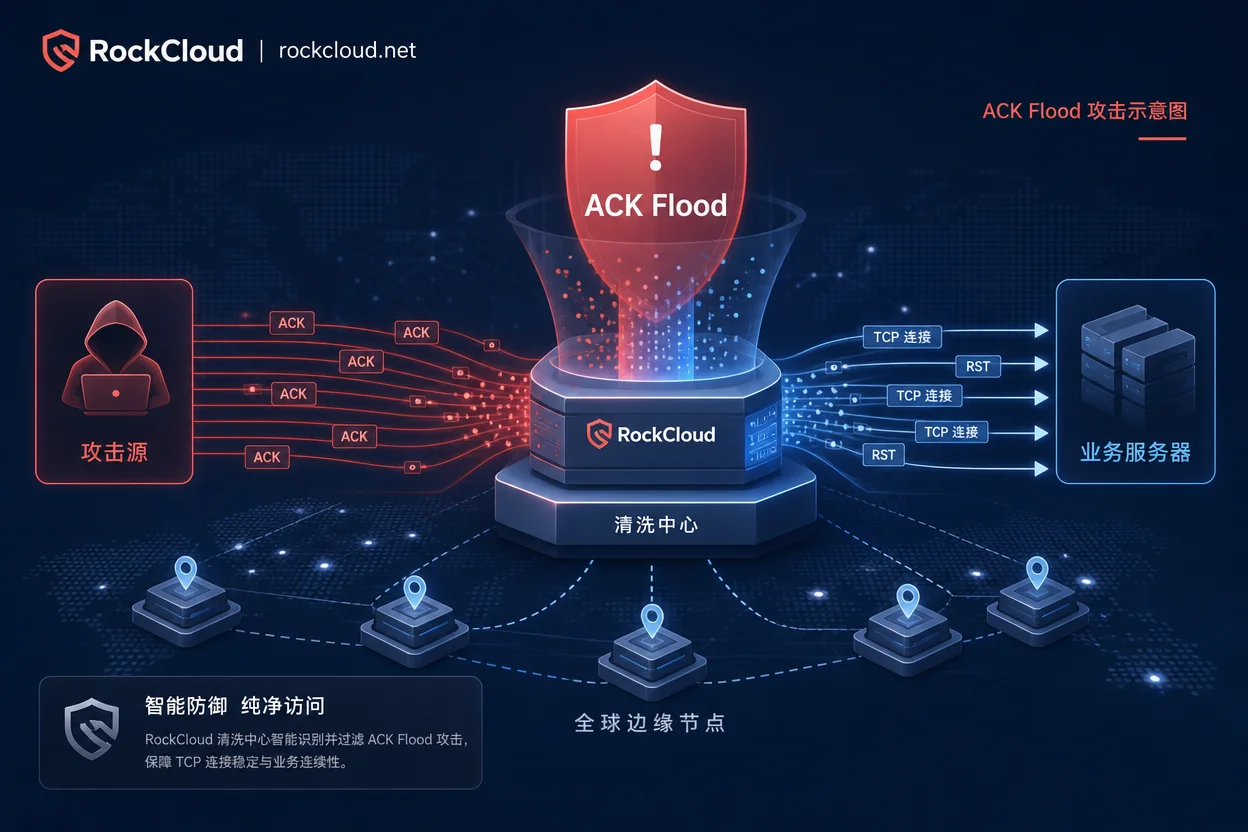
ACK Flood Attack Characteristics and Defense Strategies: Identification and Response
Learn to identify ACK Flood attacks by recognizing the fingerprint of low inbound bandwidth, high CPU, and RST spikes, and discover effective defense strategies using edge TCP termination and source whitelisting.

Dynamic CAPTCHA in Anti-CC Attack: Which Paths Trigger and What Thresholds
Effective dynamic CAPTCHA in anti-CC requires tiered triggering based on path value, using transparent checks, silent JS challenges, and interactive CAPTCHAs, adjusted automatically by anomaly signals, deployed at the edge, and clearly bounded by rate limiting and edge scrubbing.
How to Prevent Real Origin IP Exposure: 5 Leak Points to Self-Check and Origin Closures
A practical checklist to identify and close origin IP leaks, and lock down access to ensure CDN protection isn't bypassed.
NTP Reflection Amplification Attack Principles and Defense: Shut Down Amplifiers in 4 Steps
Learn how to mitigate NTP reflection amplification attacks by understanding the amplification mechanism, identifying whether you are a victim or a reflector, closing the monlist vulnerability, and moving traffic scrubbing to the network edge.