RockCloud-基石云安全-官方博客
Dedicated vs. Shared High-Protection IPs: Four Key Differences Explained
Dedicated and shared high-protection IPs differ mainly in bandwidth exclusivity, blackhole fault domain, IP reputation, and peak handling authority. This article details these four differences, backed by NETSCOUT's report on ultra-large-scale floods, and provides verification questions and red flags for pre-contract checks, along with selection guidance by business type.
ACK Flood Attack Characteristics and Defense Strategies: Identification and Response
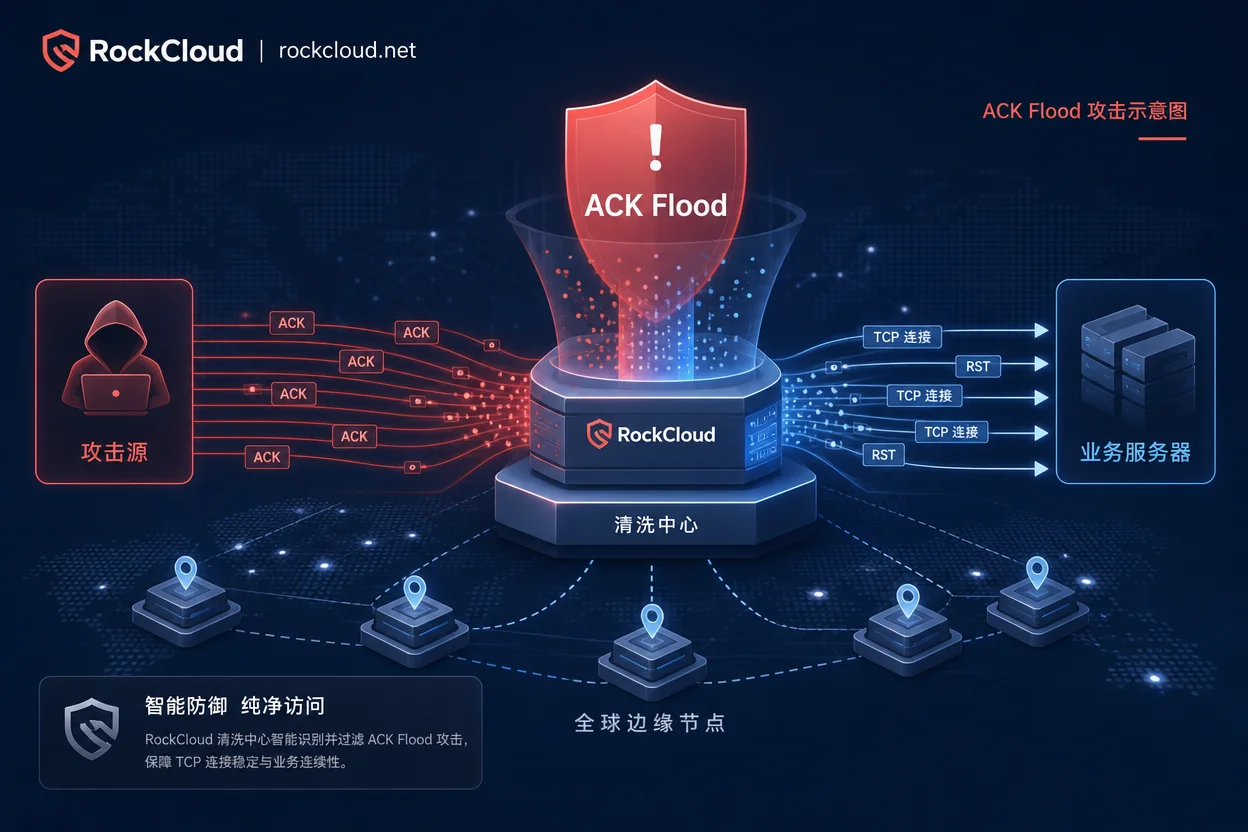
Learn to identify ACK Flood attacks by recognizing the fingerprint of low inbound bandwidth, high CPU, and RST spikes, and discover effective defense strategies using edge TCP termination and source whitelisting.
NTP Reflection Amplification Attack Principles and Defense: Shut Down Amplifiers in 4 Steps
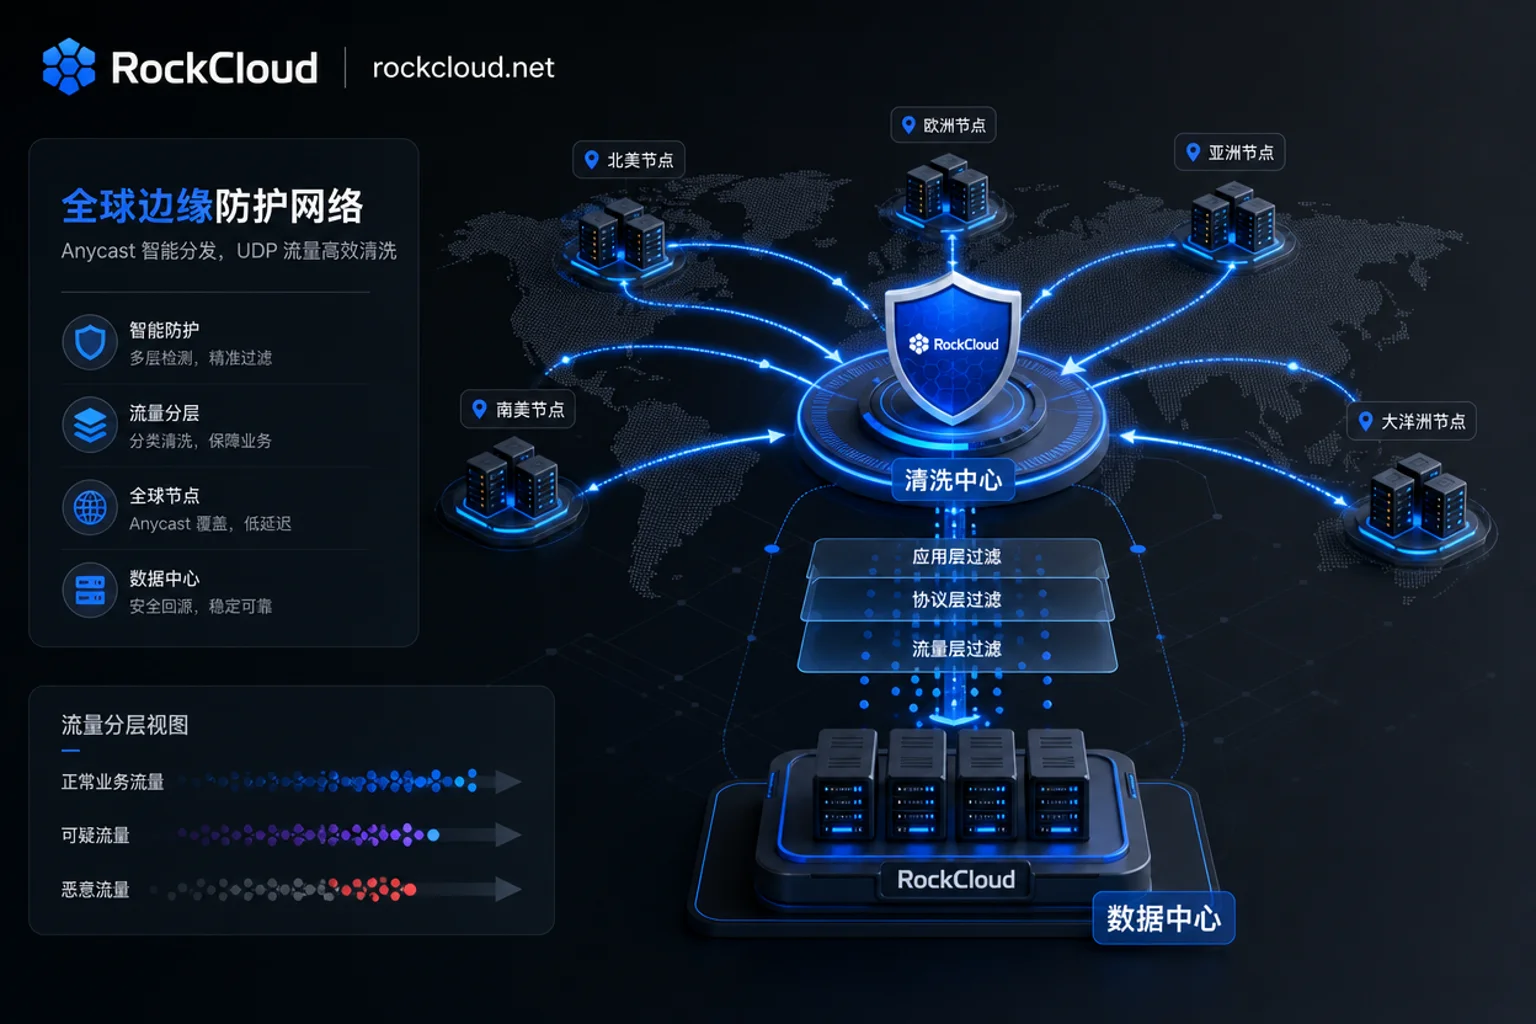
Learn how to mitigate NTP reflection amplification attacks by understanding the amplification mechanism, identifying whether you are a victim or a reflector, closing the monlist vulnerability, and moving traffic scrubbing to the network edge.
How to Handle DDoS Emergency Response? The Order of Operations Before and After Blackholing
A time-based 4-step DDoS emergency response playbook, covering attack confirmation, traffic diversion, blackhole handling, and post-recovery review, with practical checklists.
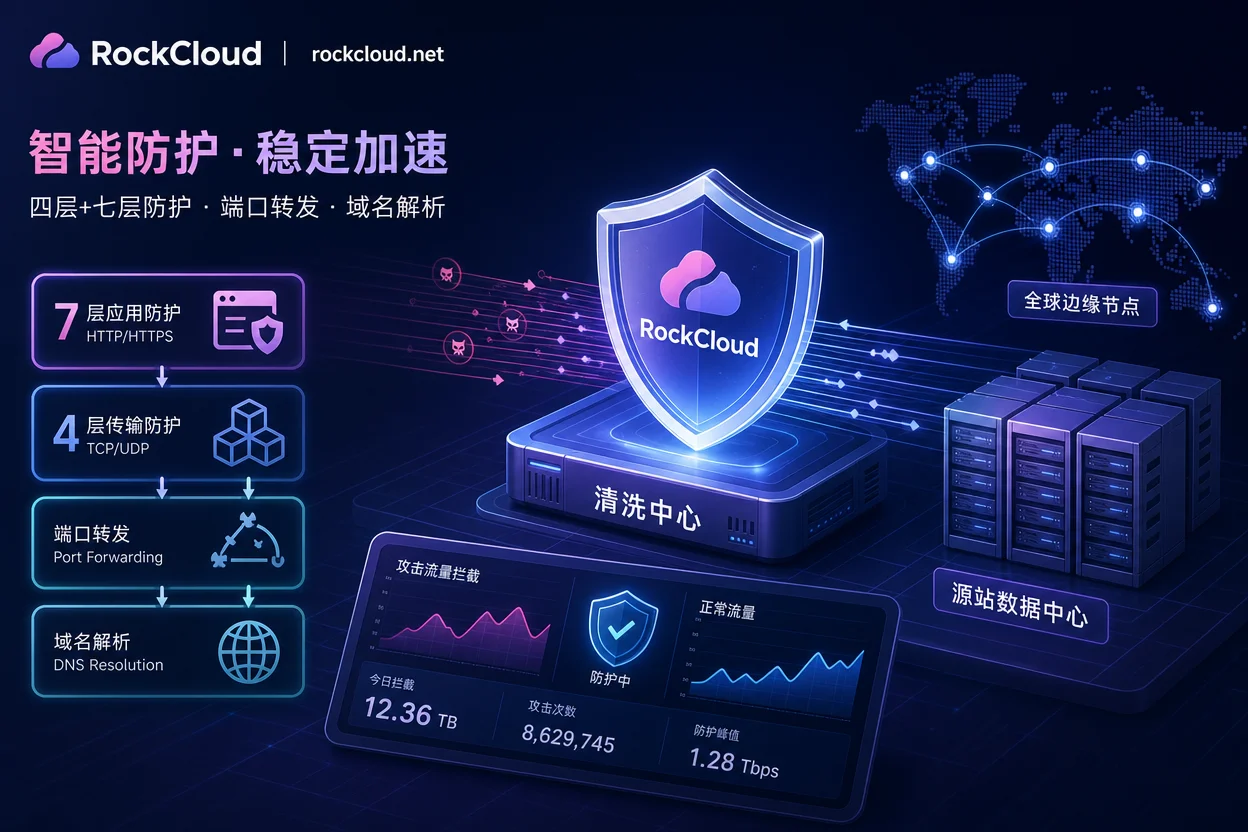
High-Protection IP vs. High-Protection CDN: Key Differences and Selection Guide for Enterprises
Understand the core differences between high-protection IP and high-protection CDN, including protocol layers, capabilities, and selection criteria for modern DDoS threats.